IOC Match Activity Searches
Search the IOC Match index to examine events logs that matched the indicators of compromise (IOC) provided by your threat intelligence feeds.
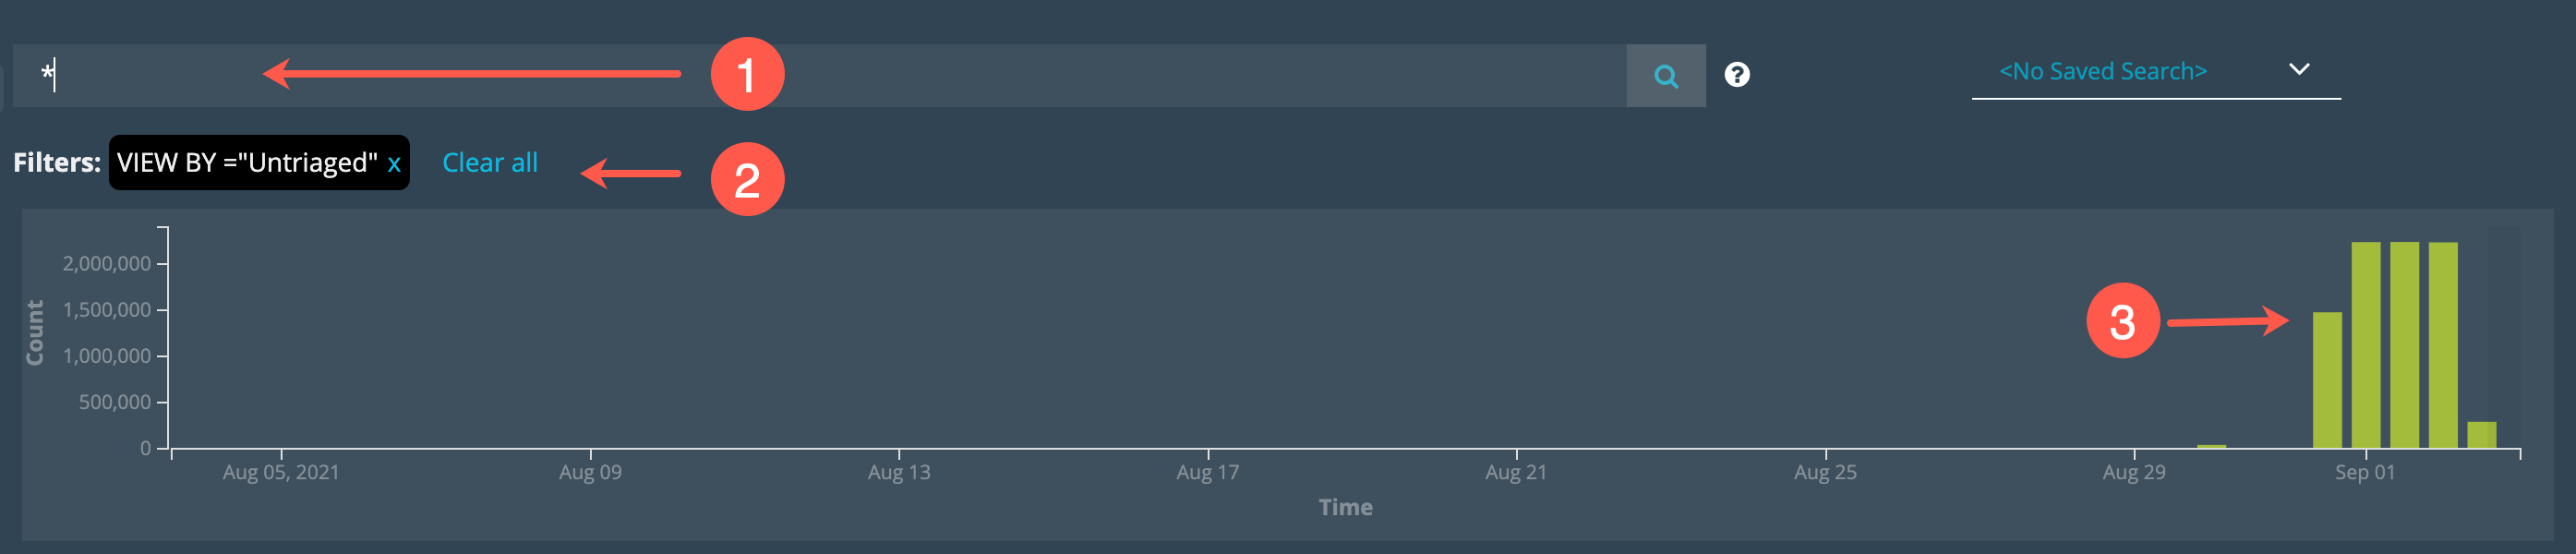

|
Search text box: Specify a keyword or field-based search expression. Keyword searches match any field. Specify field-based name-value pairs for more precise targeting. |

|
Applied Filters: Review and clear filters. |

|
Matches Timeline: Click a bar to filter by date. Click and drag over two or more bars to set a date range filter. |
About IOC Match Searches
Your organization subscribes to ThreatStream intelligence feeds that make up the set of IOCs that your organization is interested in tracking. The set of indicators are correlated with event logs when the logs are ingested. The correlated rows have both the event log fields and the threat intelligence fields. This enriched data set facilitates security analyst investigations.
During correlation, Security Analytics identifies indicators in newly received event logs. The event logs may include events forwarded from recent activity or from activity that occurred during a backfill period, depending on your Link configuration. A backfill period is an optional setting that enables the Anomali Link to ingest events from a time period before the Link was set up and activated.
IOC Match index searches are vast, but the Activity workbench has tools that make it easy for you to refine search attributes and get a targeted set of results. You can use the filter user interface (UI), as well as more advanced field-based filter expressions.
Filter UI
You can use the filter UI to apply the following filters to your search:
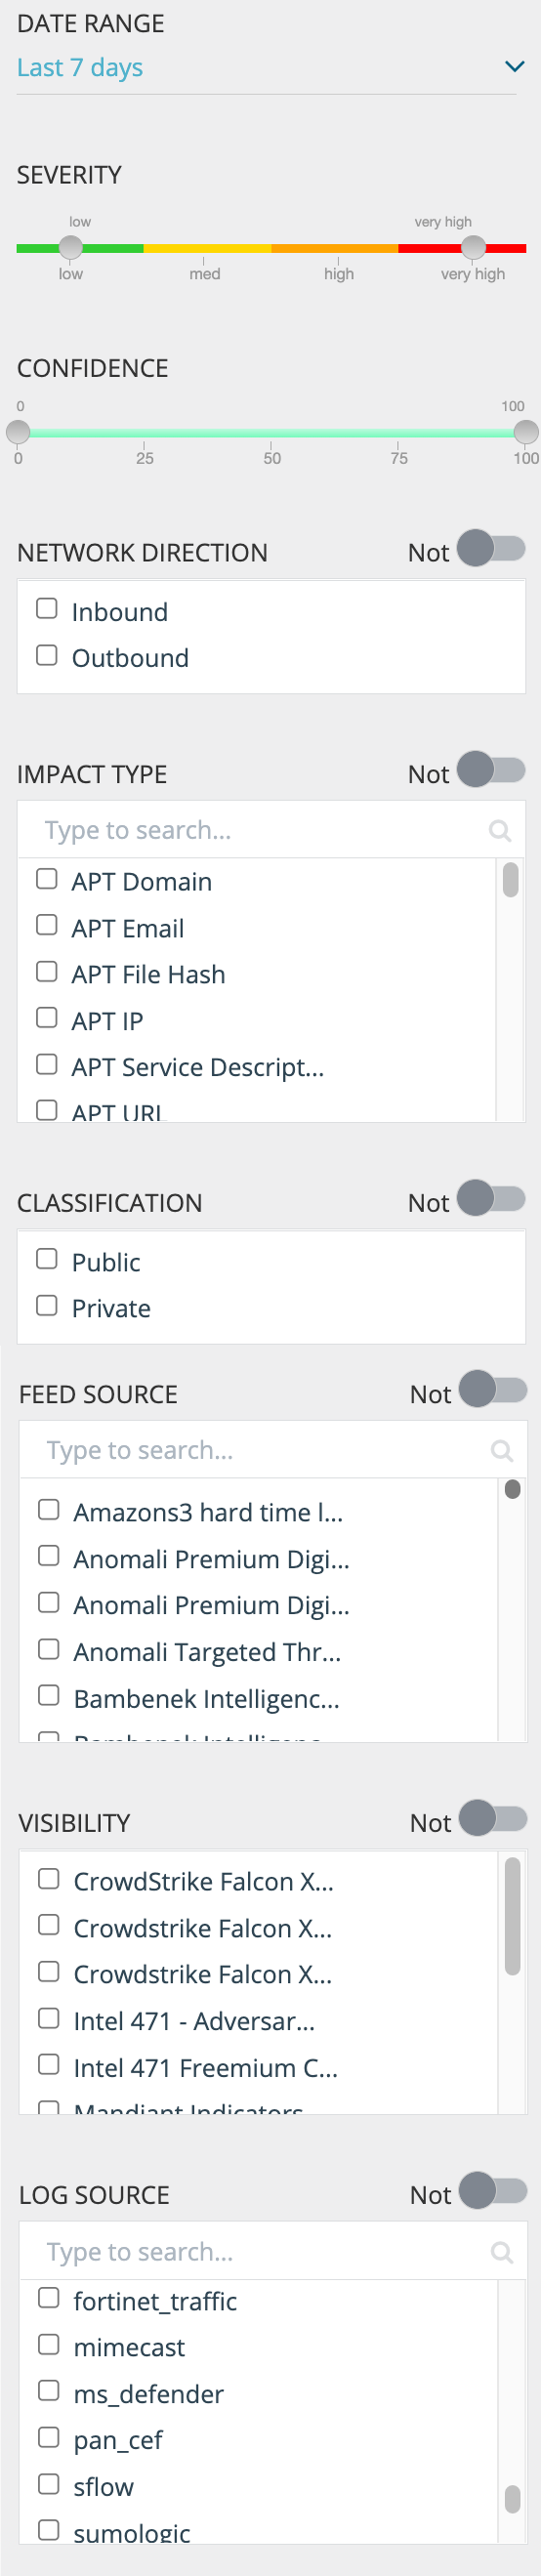
- Date Range
Select a time period, a relative expression, or a date range. The time period filter is based on event time; in other words, the timestamp in the event log.
- Severity
Use the slider to specify an event severity range or drag both ends of the slider to a single severity to filter on just one. Event severity is determined by the indicator that matched the event log.
- Confidence
Use the slider to specify a confidence score range. Confidence score indicates the certainty that an observable exhibits or is connected to malicious behavior. Confidence score is set by a ThreatStream machine learning algorithm that takes many factors into account, but can be overridden by analysts.
- Network Direction
Filter by Inbound or Outbound. Inbound and outbound are designated from the perspective of the event log source.
- Impact Type
Select an impact type. Impact type refers to the impact designated by the intelligence feed.
- Classification
Filter according to the classification designated by the intelligence feed.
- Feed Source
Select one or more intelligence feed sources.
- Visibility
Select one or more trusted circle names. Trusted circles are organizations with which the ThreatStream observable is shared.
- Log Source
Select one or more event log sources.
Note: You can use negation in search expressions by selecting the NOT operator next to the filter heading. For example, to use negation with Log Source, select the sources you do not want to search and toggle on the NOT operator next to the Log Source filter heading.
Advanced Filter Expression Examples
The following are a few example filters:
state = active AND domain startswith "qq.*"
state = active AND domain contains "*.ru"
state = active AND detail=mirai
state = active AND confidence >= 90
state = active AND confidence >= 90 AND itype = "apt_ip"
state = active AND confidence >= 90 AND (severity = "high" OR severity = "very-high")
state = active AND confidence >= 90 AND (itype = "apt_ip" OR itype = "bot_ip" OR itype = "c2_ip")
state = active AND confidence >= 70 AND (itype startswith "apt" OR itype startswith "mal" OR itype startswith "c2")
state = active AND confidence >= 75 AND itype != bot_ip AND itype != actor_ip AND itype != brute_ip
state = active AND ((itype != "bot_ip" AND confidence >= 75) OR (itype = "bot_ip" AND confidence >= 99)) AND classification = "public"
state = active AND event_time >= "2019-01-01T00:00:00"
state = active AND event.src insubnet "172.18.177.0/24"
state = active AND (itype=proxy_ip AND indicator insubnet "70.183.48.0/24")
NOT indicator insubnet "70.183.48.0/24"
trusted_circle_ids in [10028, 10029, 10030, 10031]
(confidence>=60) AND NOT trusted_circle_ids in [123, 456, 789, 890, 901, 121, 324, 356, 677, 888]
event.event_name != DnsRequest
String list:
itype in ["scan_ip","c2_domain", "c2_ip"]
Numeric list:
source_feed_id in [312, 274]
For include list information:
tags="anomali-include-list-ip"
tags="anomali-include-list-domain"
Filter Operators
The following table describes the logical operators you can use to form complex field-based search expressions. Operator names are not case sensitive.
| Field Type | Use this Operator |
|---|---|
| String |
=, !=, contains, startswith, insubnet, in (for lists) Notes:
|
| Numeric |
=, !=, <, <=, >, >=, in (for lists) For example, Note: The |
| Date | =, !=, <, <=, >, >= |
| Logical | AND, OR, NOT, (specify a parenthetical expression) |
Filter Fields
In the search box, you can specify keywords or field-value pairs. Keyword searches match any field. Specify field-based name-value pairs for more precise targeting.
The IOC Match table contains three types of fields:
- Event fields: These fields are part of the original event and are denoted by the prefix
event.<field_name>. For example,event.destdenotes the destination IP or hostname of the event. - Asset fields: These fields are added to the original event by Anomali Security Analytics during correlation. The asset data source is the data your organization provides in scanner reports or CSV files uploaded to Anomali Security Analytics. Asset fields are denoted by the prefix
asset_<field_name>. For example,asset_dest_ipdenotes the IP address for an asset that was the destination in a logged event. - Enrichment fields: These fields are added to the original event by Anomali Security Analytics during correlation to provide additional intelligence context. For example, itype, which denotes the indicator type of the event.
The following table describes all of the possible IOC Match search fields. The fields listed in the first column correspond with results table column names. The field names listed in the second column are the fields you specify when you form field-based name-value pair search expressions.
Note: Not all fields are included as columns in the results table. When you search by fields without column names, you can locate the matching values in the details page. All of the fields listed in this table can be selected when you export results.
| Column Name | Field Name |
Type | Description |
|---|---|---|---|
| Age | age | Numeric |
Indicates the age of the indicator in days. Event time - intel first seen A negative age value indicates that the event data was added to Anomali Security Analytics through backfill. |
| Link Type | app_type | String |
Link type that generated the event. Possible values: |
| ASN | asn | String | Autonomous System Number (ASN) for the IP associated with the indicator. |
| asset_dest_criticality | String |
Criticality associated with the asset that is the destination of a logged event. Possible values: critical, high, medium, low |
|
| asset_dest_dept | String |
Assigned department for an asset that is the destination of a logged event. Examples: Engineering, Finance, HR, Labs, Marketing |
|
| asset_dest_hostname | String |
Host name for an asset that is the destination of a logged event. Examples: example.local, example-pc |
|
| asset_dest_ip | String |
IP address for an asset that is the destination of a logged event. Example: 192.0.2.1 |
|
| asset_dest_location | String |
Assigned location for an asset that is the destination of a logged event. Example: Redwood City, CA |
|
| asset_dest_vulnerability | String |
Vulnerability CVE number associated with an asset that is the destination of a logged event. Examples: CVE-2021-21137, CVE-2019-3385 |
|
| Criticality | asset_src_criticality | String |
Criticality associated with the asset that is the source of a logged event. Possible values: critical, high, medium, low |
| Department | asset_src_dept | String |
Assigned department for an asset that is the source of a logged event. Examples: Engineering, Finance, HR, Labs, Marketing |
| Hostname | asset_src_hostname | String |
Host name for an asset that is the source of a logged event. Examples: example.local, example-pc |
| IP | asset_src_ip | String |
IP address for an asset that is the source of a logged event. Example: 192.0.2.1 |
| Location | asset_src_location | String |
Assigned location for an asset that is the source of a logged event. Example: Redwood City, CA |
| Vulnerability | asset_src_vulnerability | String |
Vulnerability CVE number associated with an asset that is the source of a logged event. Examples: CVE-2021-21137, CVE-2019-3385 |
| Classification | classification | String |
Indicates the confidentiality level of an indicator. Possible values: private, public Note: Private also includes Trusted Circles. |
| Confidence | confidence | Numeric |
Score from 0 to 100, as reported by the threat feed provider. |
| Match Type | corr_type | String | iocmatch |
| Count | count | Numeric | Aggregated number of events that matched the search criteria. |
| Country | country | String | Two-letter ISO country code for the IP associated with the indicator. For example, US, CN, DE, and so on. |
| Created | date_first | Date |
Timestamp of when the indicator was first seen by the threat feed provider. Notes:
|
| Modified | date_last | Date |
Timestamp of when the indicator was last seen by the threat feed provider. Notes:
|
| dcid | String | ID of the Link from which event was received. | |
| Tags | detail | String | Comments and context associated with the indicator. |
| Action | event.action | String |
Relevant for firewall and web proxy events Event log action taken by the source device; for example, |
| Answer | event.answer |
String |
Answers for the DNS query. |
| Application | event.app | String | The application detected. Example: Slack, Google Gmail, LinkedIn |
| Bytes In | event.bytes_in | Numeric |
How many bytes received by a network interface. Example: 347 |
| Bytes Out | event.bytes_out | Numeric |
How many bytes transmitted by a network interface. Example: 665 |
| Category | event.category | String |
Relevant for AWS VPC and Microsoft Defender logs. Traffic direction: ingress or egress. |
| Command Line | event.command_line | String |
The full command string of the spawned process. Example: |
| Destination | event.dest | String |
Event log destination data. The
Indicators that have IP or Domain value types can match By default, Security Analytics correlates indicators and |
| Destination IP | event.dest_ip | String |
Event log destination IP address. The Indicators that have IP value types can match By default, Security Analytics correlates indicators and |
| Destination Port | event.dest_port | Numeric |
Event log destination port. Event log destination port field. The value for |
| Data Source ID | event.ds_id | Numeric | For Universal Link log sources, this is the log source configuration ID. For Splunk log sources, this field is not applicable. |
| Data Source Type | event.ds_type | String |
Event log data source type.
Examples: |
| Event ID | event.event_id | String |
A Windows identification number that specifies the event type. Example: 4624 |
| Event Name | event.event_name | String |
The name of an event. Example: DnsRequest, ProcessRollup2 |
| Filehash | event.file_hash | String |
Event log file hash field. For example, an endpoint management application might write a log that contains file hash values. The Indicators that have Hash value types can match By default, Security Analytics correlates indicators and |
| event.file_hash2 | String | A log might have multiple file hash fields. | |
| event.file_hash3 | String | A log might have multiple file hash fields. | |
| File Name | event.file_name | String |
Event log field containing filepath. |
| File Path | event.file_path | String |
The folder containing the file. Sigma name: FilePath Example: C:\Program Files (x86)\VMware\VMware Workstation |
| Originated Host | event.host | String | Event log hostname field. For example, for events ingested from Splunk Link, the value for event.host is the hostname of the Splunk indexer that forwarded the event. |
|
HTTP Method |
event.http_method |
string |
The HTTP method used in the request. |
|
HTTP Referrer |
event.http_referrer |
string |
The HTTP referrer used in the request. |
| Image | event.image | String |
The executable name of the process. Sigma name: Image, ProcessName, OriginalFileName, TargetImage, TargetFileName Example: svchost.exe |
| Message ID | event.message_id |
String |
The globally-unique message identifier. |
| Original File Name | event.original_file_name | String |
Original name of the file that was changed. Example: "test.pdf" |
| Parent Command Line | event.parent_command_line | String |
The full command string of the parent process. Example: C:\Windows\System32\svchost.exe -k WerSvcGroup |
| Parent Image | event.parent_image | String |
The executable name of the parent process. Example: notepad.exe |
| Parent Process ID | event.parent_process_id | String |
The numeric identifier of the process assigned by the operating system. Example: 4834 |
| Platform | event.platform | String |
The operating system of the asset. Sigma name: Platform Example: win, mac, linux |
| Process ID | event.process_id |
Numeric |
The numeric identifier of the process assigned by the operating system. |
| Protocol | event.protocol | String |
Relevant for firewall and web proxy events Event log protocol field. The value for |
| DNS Query | event.query | String |
The domain that needs to be resolved in a DNS query. Example: www.google.com Note: Correlated with indicators of type domain. |
| Email Receiver | event.receiver | String |
Relevant for email-specific events Event log receiver field. The value for Indicators that have Email value types can match By default, Security Analytics correlates indicators and |
| Record Type | event.record_type |
String |
The DNS resource record type. |
| Registry Key | event.reg_key | string |
Registry key that the recorded action was applied to. Sigma name: TargetObject Example: HKEY_LOCAL_MACHINE\SOFTWARE\RegisteredApplications |
| Registry Value Name | event.reg_value_name | string |
Name of the registry value that the recorded action was applied to. Example: "Wordpad" |
| Registry Value Data | event.reg_value_data | string |
Data of the registry value that the recorded action was applied to. Example: Software\Microsoft\Windows\CurrentVersion\Applets\Wordpad |
| Email Sender | event.sender | String |
Relevant for email-specific events Event log sender field. The value for Indicators that have Email value types can match By default, Security Analytics correlates indicators and |
| Source Type | event.sourcetype | String |
Source device type that generated the event. |
| Event Source | event.src | String |
Event log source IP field. The
Indicators that have IP type or Domain value types can match By default, Security Analytics correlates indicators and |
| Source IP | event.src_ip | String |
Event log source IP field. The Indicators that have IP value types can match By default, Security Analytics correlates indicators and |
| Source Port | event.src_port | Numeric |
Relevant for firewall and web proxy events Event log source port field. The value for |
| Subject | event.subject |
String |
The subject of the message. |
| Event Time | event_time | Date |
Event log timestamp field. The value for Notes:
|
| Title | event.title | String |
Alert title (azure security alert). |
| URL | event.url.raw | String |
Relevant for firewall and web proxy events Event log URL field. The value for Indicators that have URL value types can match By default, Security Analytics correlates indicators and |
| User | event.user | String |
Relevant for firewall and web proxy events Event log user field. The value for |
| User Agent | event.user-agent | String | Event log user agent field. The value for event.user-agent is user-agent directive data in an HTTP(S) connection request—for example, Mozilla/5.0 (platform; rv:geckoversion) Gecko/geckotrail Firefox/firefoxversion. |
| Indicator | indicator | String |
Value of the indicator. This field contains the value that was matched and is always equal to the value of srcip, url, domain, md5, or email fields. |
| IOC Type | indicator_type | String |
Data type of the indicator. Possible values: ip, domain, url, email, md5 |
| iType | itype | String |
Indicator type. For example, c2_ip, compromised_email, apt_md5, and so on. See ThreatStream Indicator Types for a complete list of available indicators. |
| Latitude | lat | Numeric |
Latitude associated with the Geo location of the IP. The value displayed is rounded up to the nearest thousandth decimal place. For example: 32.789. Note: Search results are based on non-rounded values, so you might observe anomalous search results, such as a search for |
| Longitude | lon | Numeric |
Longitude associated with the Geo location of the IP. The value displayed is rounded up to the nearest thousandth decimal place. For example: 16.366. Note: Search results are based on non-rounded values, so you might observe anomalous search results, such as a search for |
| Malware Family | malware_family | String |
One or more public malware family names expected to have originated the domain. Note: Malware families are often known by multiple names or aliases. The name shown in the Anomali Security Analytics UI is one of those names or aliases. |
| originator | Numeric |
Indicates whether the connection was inbound or outbound
|
|
| Severity | severity | String |
Severity associated with the threat feed that supplied the indicator. Possible values: low, medium, high, very-high Note: The search index is tokenized. This means the text is broken down into individual terms during indexing to allow for partial matching. For example, searches for |
| Source | source.raw | String |
Name of the feed provider or organization that reported the indicator. |
| Feed | source_feed_id | Numeric | Identifier associated with the feed that contained the indicator. |
| Event Source Host | src_host | String |
An event source host value derived from asset_src_hostname, event.src, or event_ip fields, in that order. The hostname provided by the asset enrichment would be most readable, so if it data exists for it, it is used. If not, then the other source fields are evaluated. |
| State | state | String |
Current state of the indicator as reported by the threat feed. Possible values: active, inactive, falsepos |
| trusted_circle_ids | Numeric |
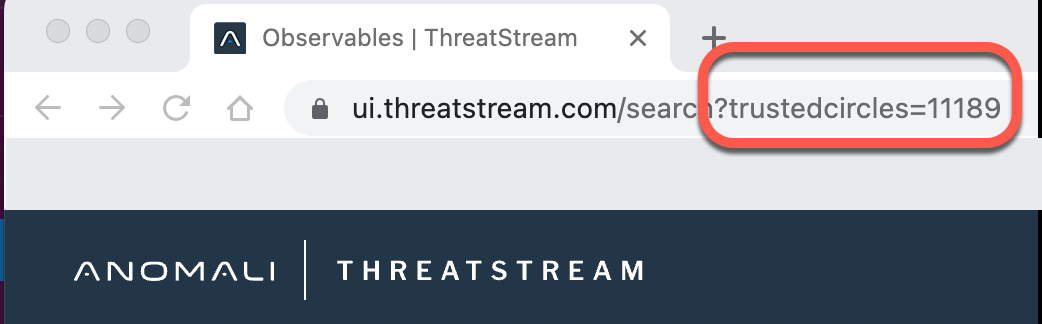
ID of the Trusted Circle with which this threat intelligence is shared on ThreatStream. To find a trusted_circle_ids value to use for Security Analytics search:
The URL parameter shows the Trusted Circle ID. For example, the following screenshot shows Trusted Circle ID 11189:
In Security Analytics results, the Visibility field on the Details page lists trusted circles data. |
IOC Match Results Table
The following figure identifies the UI elements that you use to manipulate the displayed results to find information about IOC matches.
(Click the image to enlarge it.)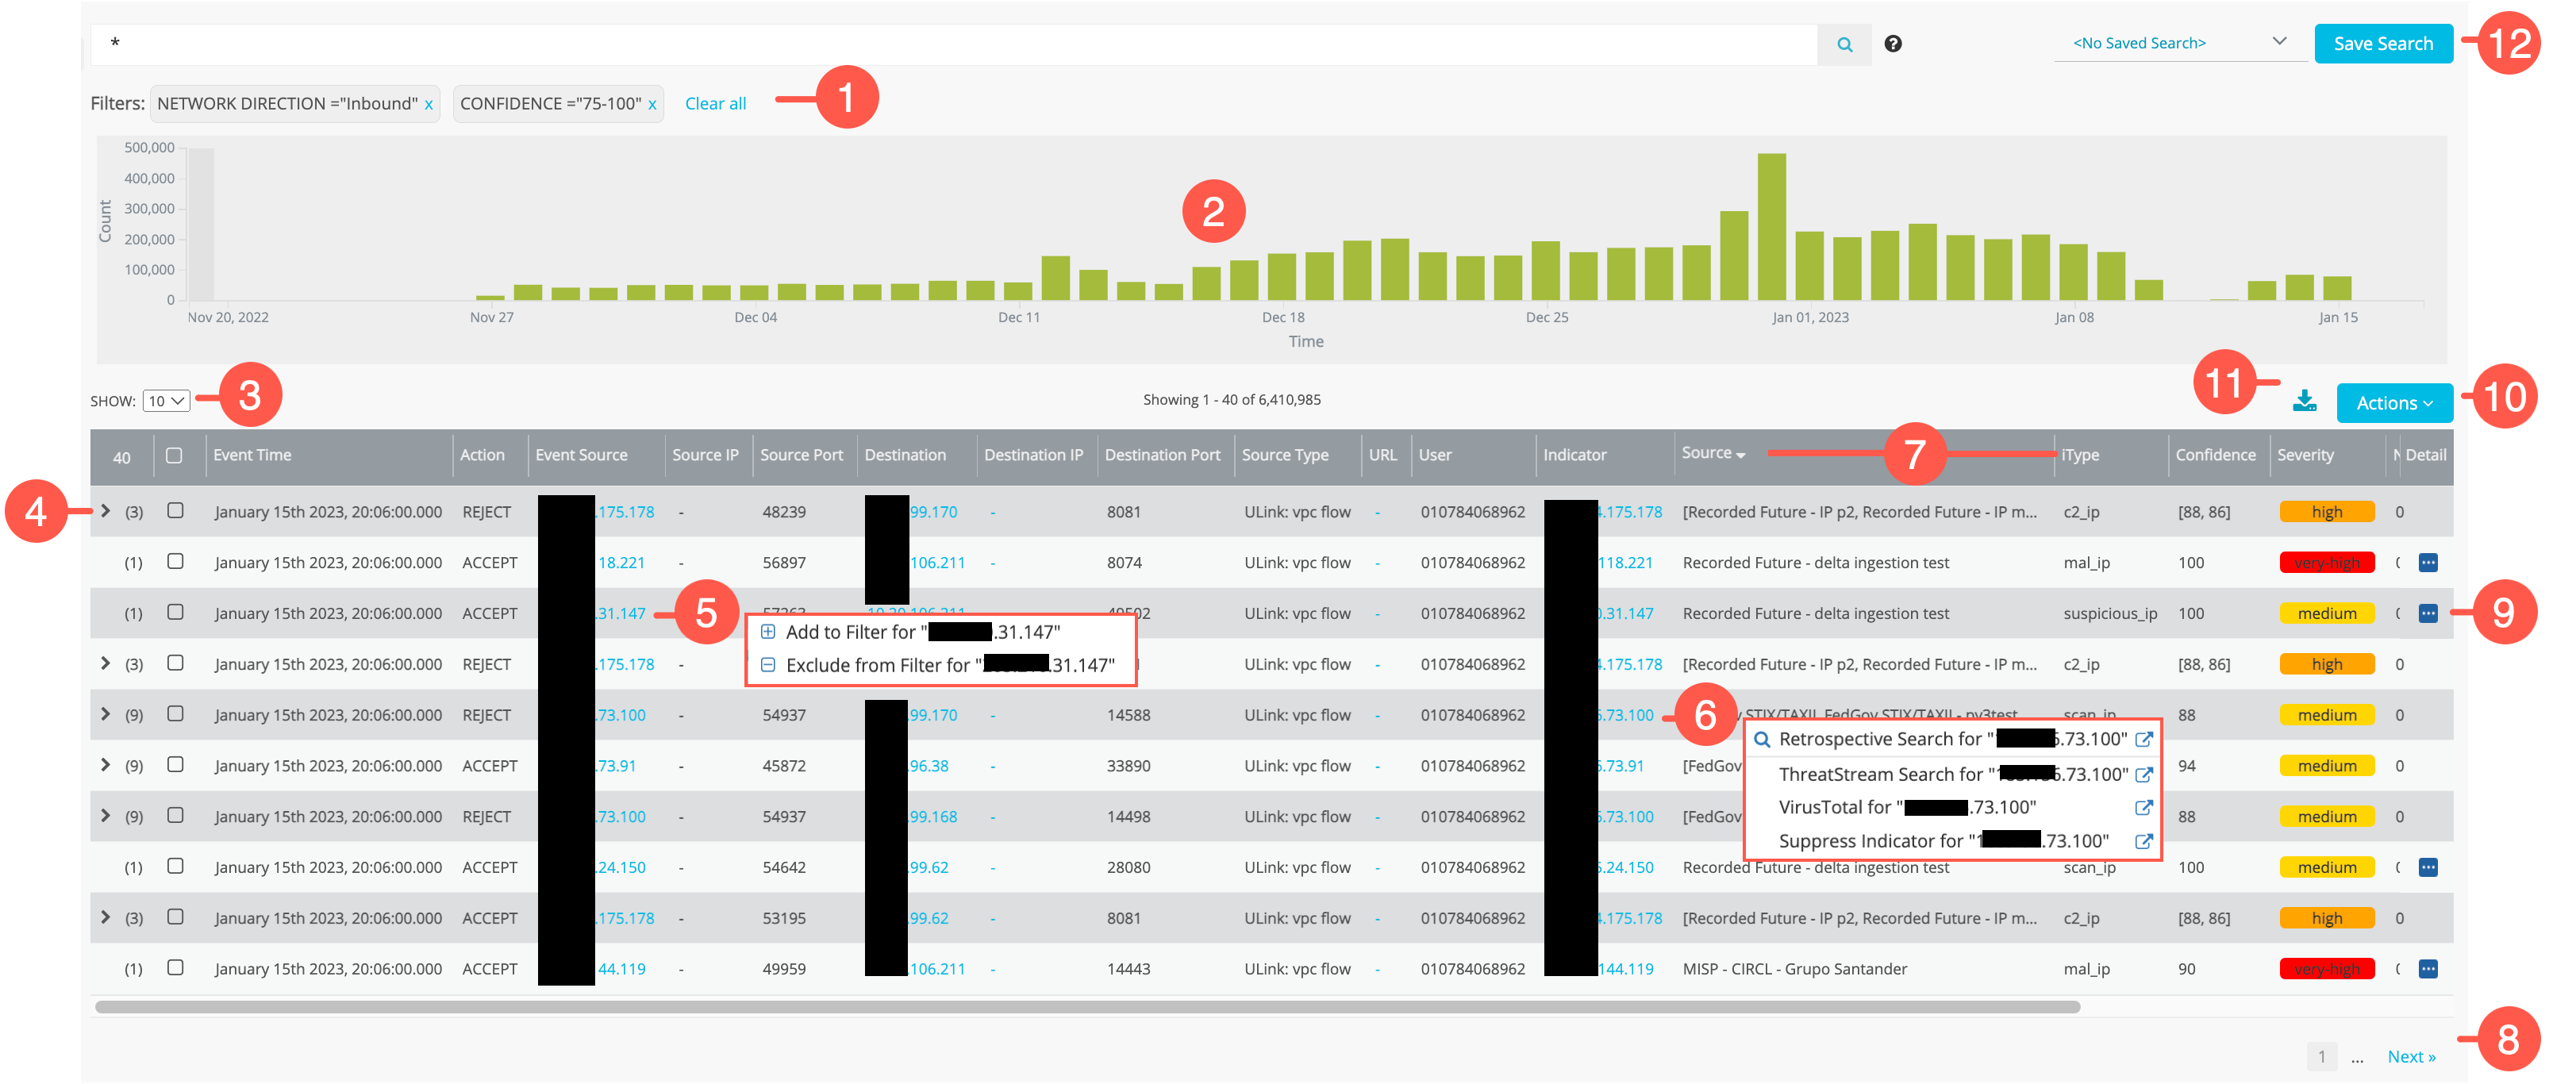

|
Review and reset applied filters. |

|
Observe the graph of matches over time. Click a bar to filter by date. Click and drag over two or more bars to set a date range filter. |

|
Select a number of rows per page. |

|
The leftmost column shows the aggregation count for the result row. Click the expander > icon to display the individual result rows. Rows are aggregated when the following fields are identical: event_time, event.action, event.src, event.src_ip, event.src_port, event.dest, event.dest_ip, and event.dest_port. This occurs when an event log matches more than one indicator or when an indicator has multiple intel source feeds. |

|
Option-click a value and select an option to apply a filter that requires or excludes rows matching the value. Not all fields support filtering from the results grid. |

|
Click a hyperlinked value and select an option to search ThreatStream, search VirusTotal, run a retrospective search, or add the field value to a Security Analytics Exclude List. The availability of options depend on the data. For example, you can add an indicator value to the Suppressed Indicators list; you can a destination IP address for IP addresses in your local network to the Asset Exclude list. |

|
Click the column header to sort the rows in ascending or descending order according to values in the column. Click a column header divider and drag it to make a column wider or more narrow. |

|
Go to the next page of results or another page by page number. |

|
Display the Details page for the matched event. See View Match Details. |

|
Perform an action related to the selected row. See Perform Actions. |

|
Export the results table. See Export Search Results. |

|
Create a Saved Search configuration. See Saved Searches. |
Perform Actions
The Action menu above the results table allows you to perform the following actions.
| Action | Description |
|---|---|
| Configure Fields | Select this option to configure the fields (columns) that appear in the results table. |
| Retrospective Search | Select this option to perform a retrospective search for the indicator correlated with the event. |
| Investigate |
Select this option to add the result to a ThreatStream investigation. Configure one of the following choices:
Note: For information about ThreatStream investigations, refer to the ThreatStream online help. |
| Suppress Indicators | Select this option to add the indicator to the indicator exclude list. |
View Match Details

|
Click the Details icon in the right-most column to display the details page. |
The following figure identifies the UI elements that you use to find information on the IOC Match Details page.
|
|
Open ThreatStream to view ThreatStream reports about the indicator. |
|
|
Review the indicator details and event details correlated in Security Analytics. |
|
|
Use the tabs to learn more:
|
|
|
Use the tabs to review associated ThreatStream threat model entities and investigations. |
|
|
Click Actions and select Add to Investigation to add the log to a ThreatStream investigation. Note: For information about ThreatStream investigations, refer to the ThreatStream online help. |
|
|
Click the X to exit the details page and return to the results table. |