DGA Match Activity Searches
Search the DGA Match index to examine events logs that matched domains deemed likely Domain Generated Algorithm (DGA) domains.
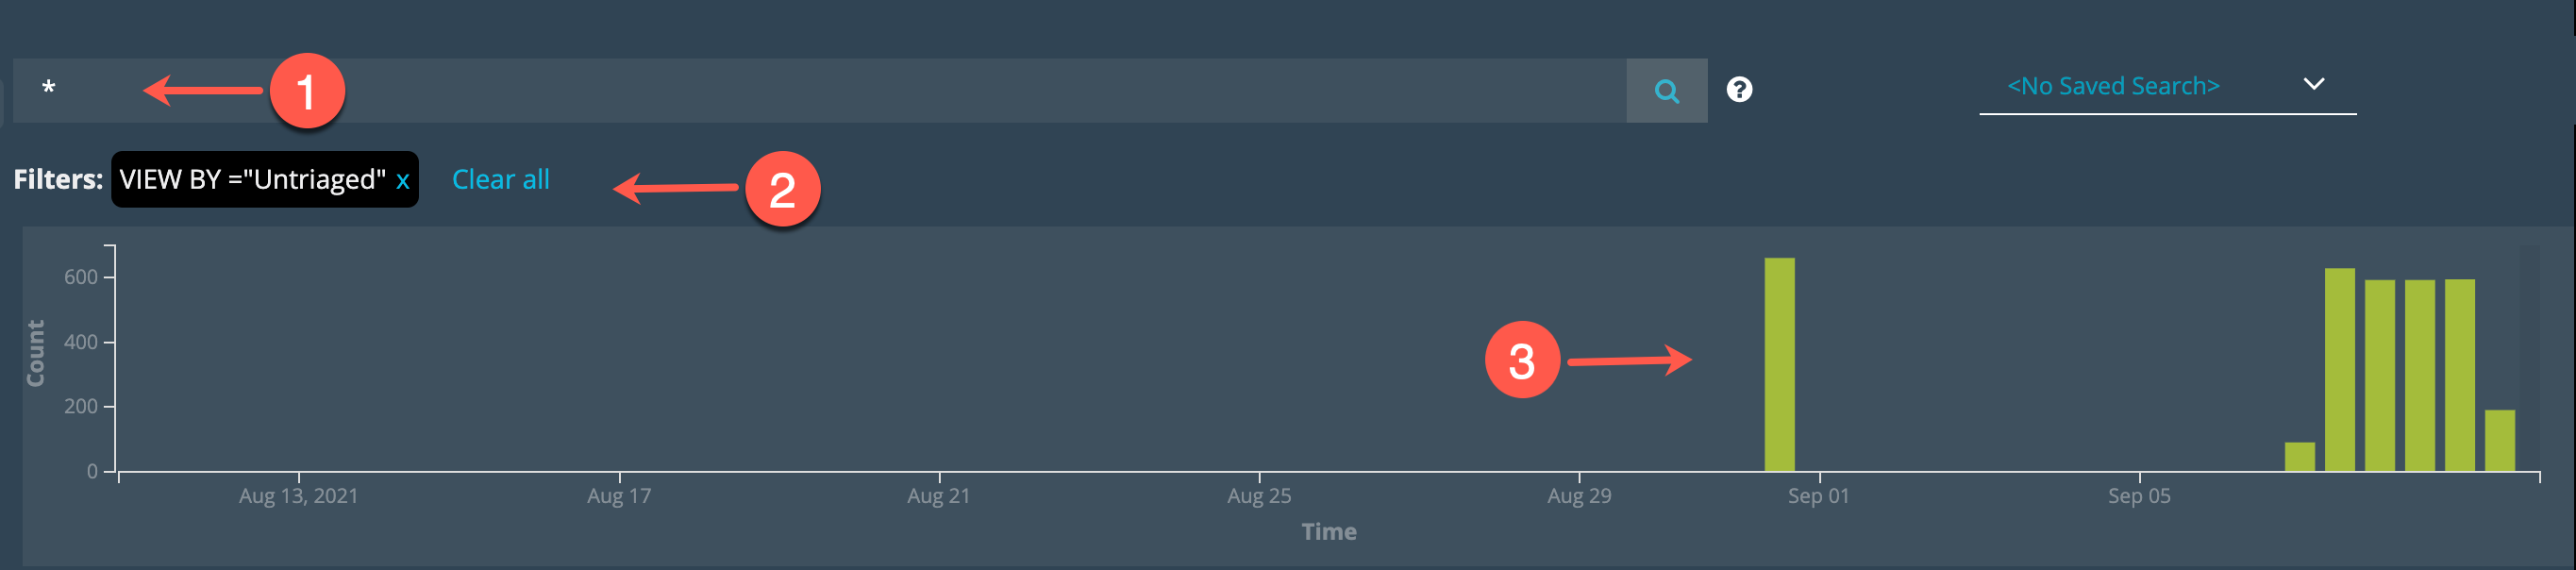

|
Search text box: Specify a keyword or field-based search expression. Keyword searches match any field. Specify field-based name-value pairs for more precise targeting. |

|
Applied Filters: Review and clear filters. |

|
Matches Timeline: Click a bar to filter by date. Click and drag over two or more bars to set a date range filter. |
About DGA Match Searches
Anomali Security Analytics automatically processes domain names (contained in the host names and URLs) in the events received from your network to determine the likelihood of these being DGA domains. The Anomali Security Analytics DGA processor uses machine learning to calculate the probability of a domain in an event being a DGA domain. Domains with a probability of 60% or higher are considered "likely DGAs". The Security Analytics DGA processor further corroborates the state of a domain against other data sources before classifying the domain state as active or benign. An active domain has a high probability as generated with a DGA, while a benign domain is most likely not generated by a DGA.
Security Analytics generates matches for active DGA domains. The machine learning engine continuously updates the state of a domain as Security Analytics ingests domain information.
Anomali Security Analytics does not generate DGA matches for domains determined to be benign or false positives.
Filter UI
You can use the filter UI to apply the following filters to your search:
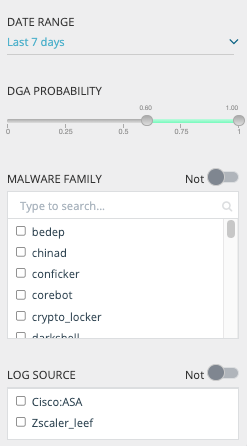
- Date Range
Select a time period, a relative expression, or a date range. The time period filter is based on event time; in other words, the timestamp in the event log.
- DGA Probability
Use the slider to specify a DGA probability range.
- Malware Family
Malware family is a name given to multiple file artifacts that have significant code similarities and are distinct enough from other groups of known malware. Malware families are often known by multiple names or aliases. Select one or more malware families.
- Log Source
Select one or more event log sources.
Note: You can use negation in search expressions by selecting the NOT operator next to the filter heading. For example, to use negation with Log Source, select the sources you do not want to search and toggle on the NOT operator next to the Log Source filter heading.
Filter Examples
The following are a few example filters:
dga_prob >= .80
dga_prob > 0.5 AND dga_prob < 0.8
state = active AND event.dest = "qukaheylka.xyz"
event.url.raw="http://tsrs.pw/"
event.user="barbe_meletius@live.com"
malware_family startswith conficker
malware_family in ["Gameover_DGA", "Emotet.c"]
event.sourcetype contains cisco
dga_prob >= .80 and event.sourcetype != cisco
dga_prob >= .80 and (event.sourcetype = Zscaler or leef)
dga_prob >= .80 and ((event.sourcetype = Zscaler or leef) and (user !="user6@acme.com"))
Filter Operators
The following table describes the logical operators you can use to form complex field-based search expressions. Operator names are not case sensitive.
| Field Type | Use this Operator |
|---|---|
| String |
=, !=, contains, startswith, insubnet, in (for lists) Notes:
|
| Numeric |
=, !=, <, <=, >, >=, in (for lists) For example, Note: The |
| Date | =, !=, <, <=, >, >= |
| Logical | AND, OR, NOT, (specify a parenthetical expression) |
Filter Fields
The DGA Match table contains two types of fields:
- Event fields: These fields are part of the original event and are denoted by the prefix
event.<field_name>. For example,event.destdenotes the destination IP or hostname of the event. - Enrichment fields: These fields are added to the original event by Anomali Security Analytics during correlation to provide additional intelligence context. For example, itype, which denotes the indicator type of the event.
The following table describes all of the possible search fields. The fields listed in the first column correspond with results table column names. The field names listed in the second column are the fields you specify when you form field-based name-value pair search expressions.
Note: Not all fields are included as columns in the results table. When you search by fields without column names, you can locate the matching values in the details page. All of the fields listed in this table can be selected when you export results.
| Column Name | Field Name |
Type | Description |
|---|---|---|---|
| Age | age |
Does not apply to the DGA Match index. |
|
| app_type | String | Link type that generated the event. | |
| ASN | asn | Does not apply to the DGA Match index. | |
| asset_dest_criticality | String |
Does not apply to the DGA Match index. |
|
| asset_dest_dept | String |
Does not apply to the DGA Match index. |
|
| asset_dest_hostname | String |
Does not apply to the DGA Match index. |
|
| asset_dest_ip | String |
Does not apply to the DGA Match index. |
|
| asset_dest_location | String |
Does not apply to the DGA Match index. |
|
| asset_dest_vulnerability | String |
Does not apply to the DGA Match index. |
|
| asset_src_criticality | String |
Does not apply to the DGA Match index. |
|
| asset_src_dept | String |
Does not apply to the DGA Match index. |
|
| Hostname | asset_src_hostname | String |
Does not apply to the DGA Match index. |
| asset_src_ip | String |
Does not apply to the DGA Match index. |
|
| asset_src_location | String |
Does not apply to the DGA Match index. |
|
| asset_src_vulnerability | String |
Does not apply to the DGA Match index. |
|
| Classification | classification | String |
Does not apply to the DGA Match index. |
| Confidence | confidence | Numeric |
Does not apply to the DGA Match index. |
| Count | count | Numeric | Aggregated number of events that matched the search criteria. |
| Country | country | Does not apply to the DGA Match index. | |
| Created | date_first | Date |
Does not apply to the DGA Match index. |
| Modified | date_last | Date |
Does not apply to the DGA Match index. |
| dcid | String | ID of the Link from which event was received. | |
| Tags | detail | String |
Does not apply to the DGA Match index. |
| DGA Probability | dga_prob | Numeric |
Probability based on Anomali Security Analytics's DGA algorithm that the domain in the event is a DGA domain. |
| DGA TAG | dga_tag | String |
Does not apply to the DGA Match index. |
| Action | event.action | String |
Relevant for firewall and web proxy events Event log action taken by the source device; for example, |
| Application | event.app | String |
The application detected. Example: ProcDump |
| Bytes In | event.bytes_in | Numeric |
How many bytes received by a network interface. Example: 347 |
| Bytes Out | event.bytes_out | Numeric |
How many bytes transmitted by a network interface. Example: 665 |
| Category | event.category | String |
Relevant for AWS VPC and Microsoft Defender logs. Traffic direction: ingress or egress. |
| Command Line | event.command_line | String |
The full command string of the spawned process. Example: |
| Destination | event.dest | String |
Event log destination data. The
Indicators that have IP or Domain value types can match By default, Security Analytics correlates indicators and |
| Destination IP | event.dest_ip |
Event log destination IP address. The Indicators that have IP value types can match By default, Security Analytics correlates indicators and |
|
| Destination Port | event.dest_port | Numeric |
Does not apply to the DGA Match index. |
| event.ds_id | Does not apply to the DGA Match index. | ||
| Data Source Type | event.ds_type | String |
Event log data source type. Examples: az_sentinel, qradar |
| Event ID | event.event_id | String |
A Windows identification number that specifies the event type. Example: 4624 |
| Event Name | event.event_name | String |
The name of an event. Example: DnsRequest, ProcessRollup2 |
| File Hash | event.file_hash | String |
Event log file hash field. For example, an endpoint management application might write a log that contains file hash values. The Indicators that have Hash value types can match By default, Security Analytics correlates indicators and |
| event.file_hash2 | String | A log might have multiple file hash fields. | |
| event.file_hash3 | String | A log might have multiple file hash fields. | |
| File Name | event.file_name | String |
Does not apply to the DGA Match index. |
| Host | event.host | String | Event log hostname field. For example, for events ingested from Splunk Link, the value for event.host is the hostname of the Splunk indexer that forwarded the event. |
| Image | event.image | String |
The executable name of the process. Sigma name: Image, ProcessName, OriginalFileName, TargetImage, TargetFileName Example: svchost.exe |
| Message ID | event.message_id |
String |
The globally-unique message identifier. |
| Original File Name | event.original_file_name | String |
Original name of the file that was changed. Example: "test.pdf" |
| Parent Command Line | event.parent_command_line | String |
The full command string of the parent process. Example: C:\Windows\System32\svchost.exe -k WerSvcGroup |
| Parent Image | event.parent_image | String |
The executable name of the parent process. Example: notepad.exe |
| Parent Process ID | event.parent_process_id | String |
The numeric identifier of the process assigned by the operating system. Example: 4834 |
| Platform | event.platform | String |
The operating system of the asset. Sigma name: Platform Example: win, mac, linux |
| Parent Process ID | event.parent_process_id | String |
The numeric identifier of the process assigned by the operating system. Example: 4834 |
| Protocol | event.protocol | String |
Relevant for firewall and web proxy events Event log protocol field. The value for |
| DNS Query | event.query | String |
The domain that needs to be resolved in a DNS query. Example: www.google.com Note: Correlated with indicators of type domain. |
| Email Receiver | event.receiver | String |
Does not apply to the DGA Match index. |
| Record Type | event.record_type |
String |
The DNS resource record type. |
| Registry Key | event.reg_key | string |
Registry key that the recorded action was applied to. Sigma name: TargetObject Example: HKEY_LOCAL_MACHINE\SOFTWARE\RegisteredApplications |
| Registry Value Name | event.reg_value_name | string |
Name of the registry value that the recorded action was applied to. Example: "Wordpad" |
| Registry Value Data | event.reg_value_data | string |
Data of the registry value that the recorded action was applied to. Example: Software\Microsoft\Windows\CurrentVersion\Applets\Wordpad |
| Email Sender | event.sender | String |
Relevant for email-specific events Event log sender field. The value for Indicators that have Email value types can match By default, Security Analytics correlates indicators and |
| Source Type | event.sourcetype | String |
Source device type that generated the event. |
| Event Source | event.src | String |
Event log source IP field. The
Indicators that have IP type or Domain value types can match By default, Security Analytics correlates indicators and |
| Source IP | event.src_ip | String |
Does not apply to the DGA Match index. |
| Source Port | event.src_port | Numeric |
Does not apply to the DGA Match index. |
| Event Time | event_time | Date |
Event log timestamp field. The value for Notes:
|
| Title | event.title | String |
Alert title (azure security alert). |
| URL | event.url.raw | String |
Relevant for firewall and web proxy events Event log URL field. The value for Indicators that have URL value types can match By default, Security Analytics correlates indicators and |
| User | event.user | String |
Relevant for firewall and web proxy events Event log user field. The value for event.user is the username associated with an authenticated HTTP(S) connection request—for example, |
| User Agent | event.user-agent | String | Does not apply to the DGA Match index. |
| Indicator | indicator | String |
Value of the indicator. This field contains the value that was matched and is always equal to the value of srcip, url, domain, md5, or email fields. |
| indicator_type | String |
Data type of the indicator. Possible values: ip, domain, url, email, md5 |
|
| iType | itype | String | Does not apply to the DGA Match index. |
| Latitude | lat | Numeric |
Does not apply to the DGA Match index. |
| Location | loc | Does not apply to the DGA Match index. | |
| Longitude | lon | Numeric |
Does not apply to the DGA Match index. |
| Malware Family | malware_family | String |
One or more public malware family names expected to have originated the domain. Note: Malware families are often known by multiple names or aliases. The name shown in the Anomali Security Analytics UI is one of those names or aliases. |
| originator | Numeric |
Indicates whether the connection was inbound or outbound
|
|
| Severity | severity | String | Does not apply to the DGA Match index. |
| source.raw | String | Does not apply to the DGA Match index. | |
| Feed | source_feed_id | Numeric | Does not apply to the DGA Match index. |
| Event Source Host | src_host | String |
An event source host value derived from the event.src field. |
| State | state | String |
Current state of the domain either as determined by the Anomali Security Analytics's DGA engine or marked by user. Possible values: active, benign, falsepos |
| trusted_circle_ids | Numeric | Does not apply to the DGA Match index. | |
| trusted_circle_names | String | Does not apply to the DGA Match index. |
DGA Match Results Table
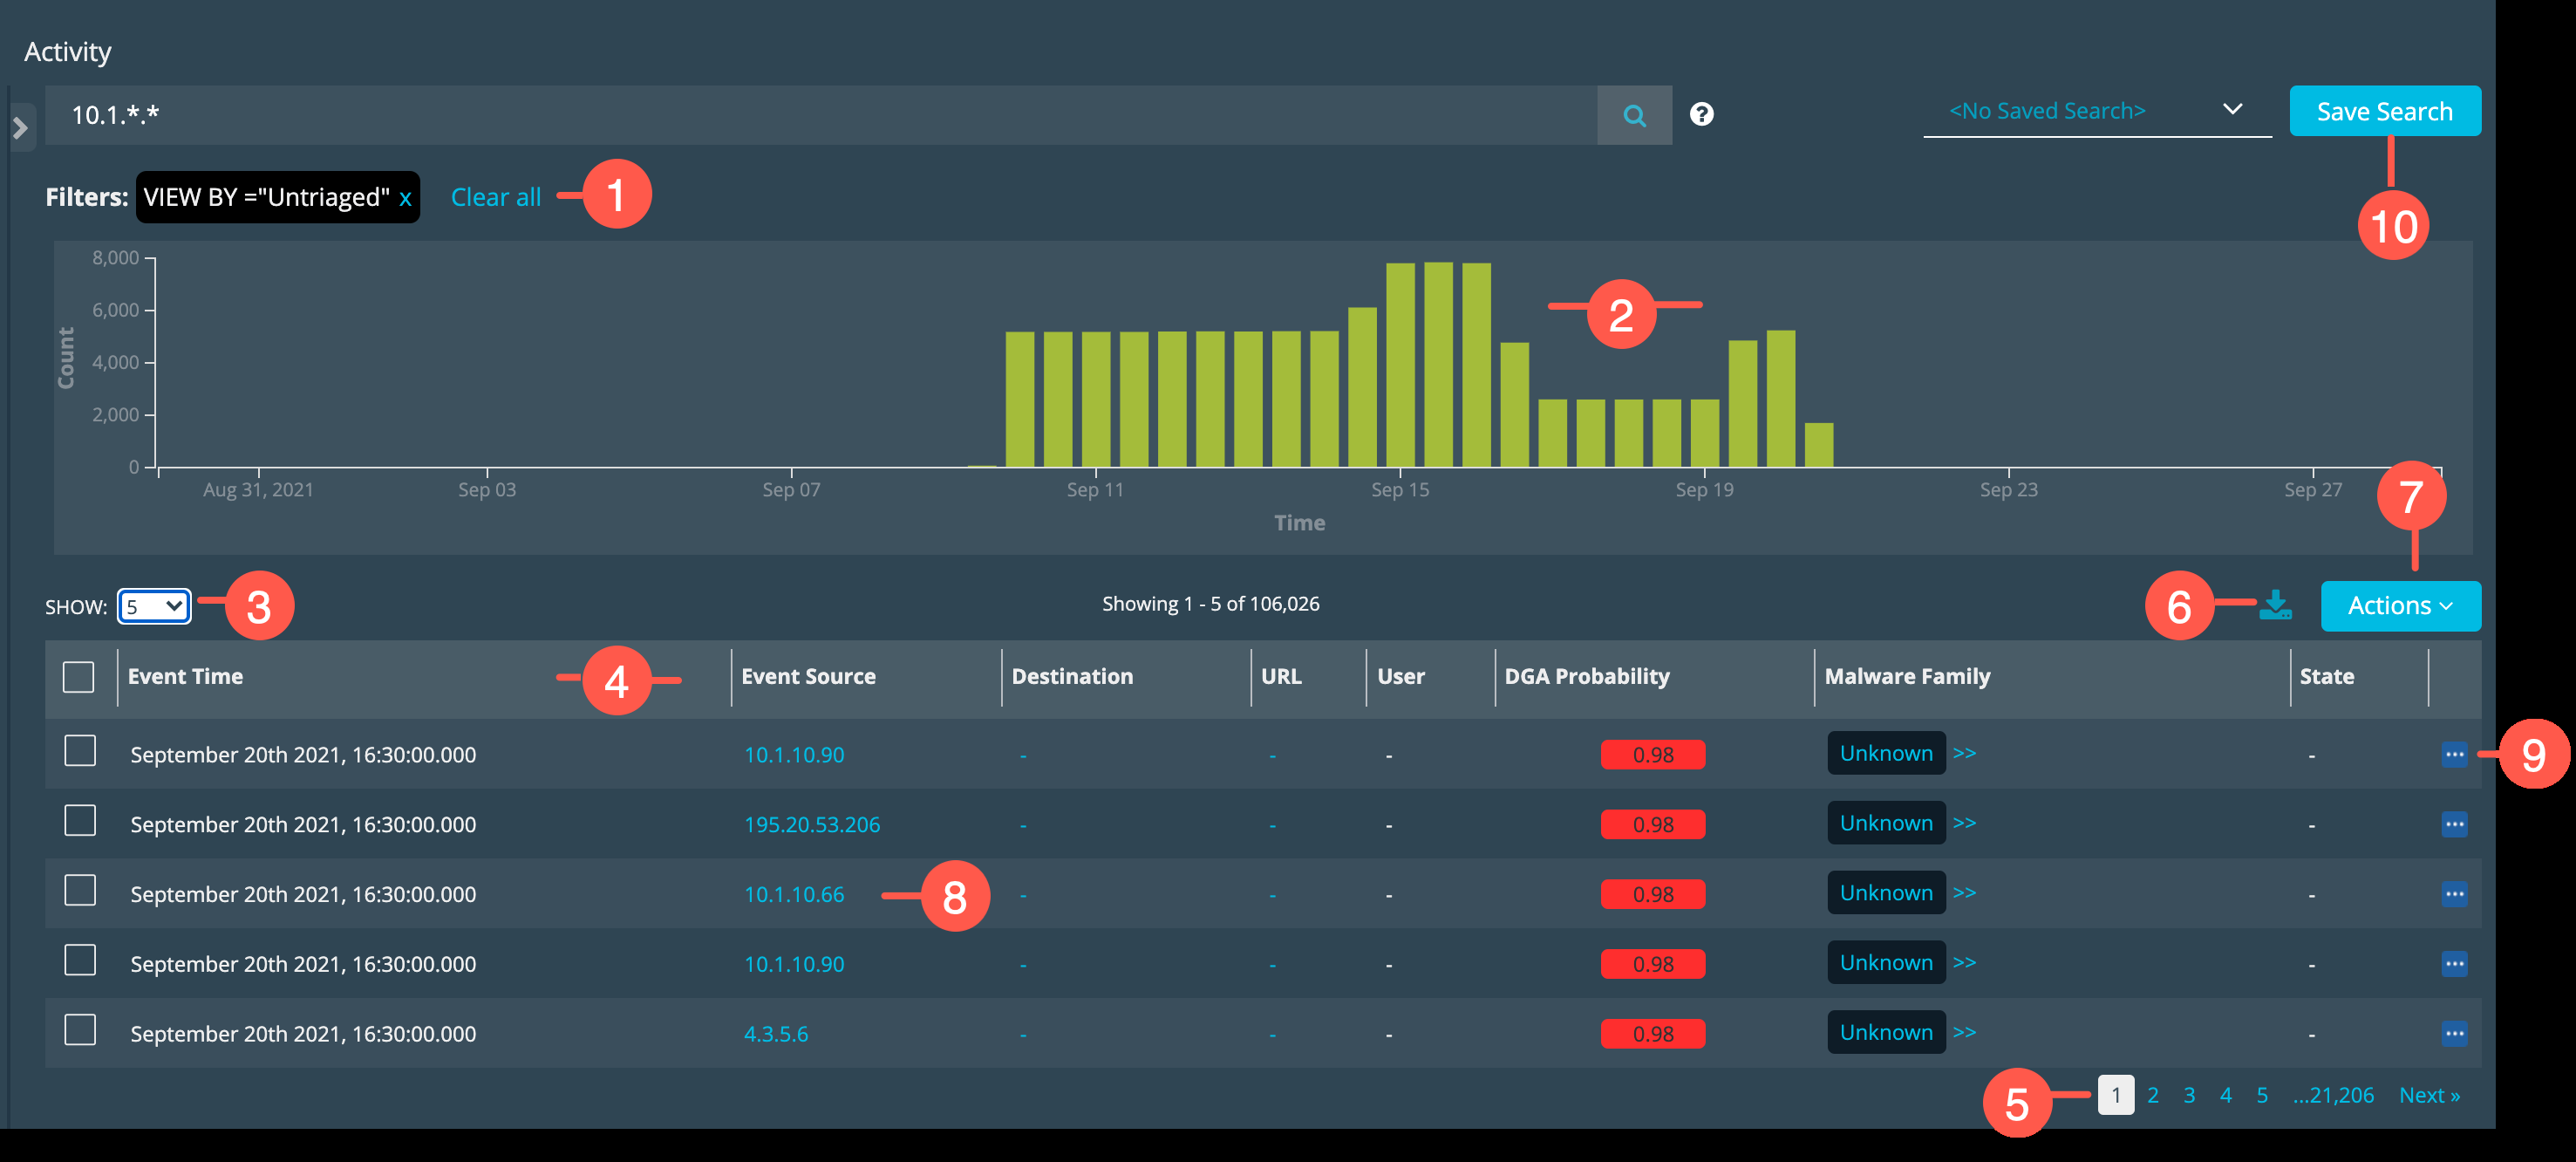
The following figure identifies the UI elements that you use to manipulate the displayed results to find information about DGA matches.

|
Review and reset applied filters. |

|
Observe the graph of matches over time. |

|
Select a number of rows per page. |

|
Click the column header to sort the rows in ascending or descending order according to values in the column. Click a column header divider and drag it to make a column wider or more narrow. |

|
Go to the next page of results or another page by page number. |

|
Export the results table. See Export Search Results. |

|
Perform an action related to the selected row. See Perform Actions. |

|
Click a hyperlinked value and select an option to run a Security Analytics retrospective search or search VirusTotal. |

|
Display the Details page for the matched event. See View Match Details. |

|
Create a Saved Search configuration. See Saved Searches. |
Perform Actions
The Action menu above the results table allows you to perform the following actions.
| Action | Description |
|---|---|
| Configure Fields | Select this option to configure the fields (columns) that appear in the results table. |
| Retrospective Search | Select this option to perform a retrospective search for the indicator correlated with the event. |
| Investigate |
Select this option to add the result to a ThreatStream investigation. Configure one of the following choices:
Note: For information about ThreatStream investigations, refer to the ThreatStream online help. |
| Mark As False Positive | Select this option to add the indicator to the DGA exclude list. |
View Match Details

|
Click the Details icon in the right-most column to display the details page. |
The following figure identifies the UI elements that you use to find information on the DGA Match Details page.
|
|
Review the indicator details and event details correlated in Security Analytics. |
|
|
Use the tabs to learn more:
|
|
|
Select Mark As False Positive or click Actions and select Add to Investigation to add the log to a ThreatStream investigation. Note: For information about ThreatStream investigations, refer to the ThreatStream online help. |
|
|
Click the X to exit the details page and return to the results table. |