NSG Flow 
Anomali supports the ingestion of NSG Flow logs through the Azure Storage Account.
Azure Storage Account
You can use your existing Azure Storage Account or create a new Azure Storage Account to add a new log source in the Anomali platform.
Onboarding steps
Prerequisites
-
An active Azure subscription.
Step 1: Register Insights Provider
See Microsoft's guide to Register Insights Provider for more information.
Step 2: Azure storage account
If you don't have an Azure storage account, see Microsoft's guide to Create an Azure storage account.
If the account exists, proceed to Step 3: Obtain Account Access Key.
Step 3: Obtain Account Access Key
-
Sign into the Azure portal.
-
Navigate to Storage account and select your account.
-
In the Security + networking section, navigate to the Access keys setting.
-
Click Show Keys.
-
Copy the access key and note the corresponding Storage Account Name.
Step 4: Add NSG Flow as new log source
To add NSG Flow as a new log source on the Anomali platform:
-
Navigate to Search > Log Source Management.
-
Click New to add a new log source.
-
Enter a name for the log source.
-
(Optional) Enter a description for the log source.
-
Select NSG Flow as the source type.
-
Select API as the ingestion method.
-
Select API as the ingest method.
-
Provide the Basic Configuration details:
-
Azure Storage Account Name: Enter the storage account name you obtained in Step 3: Obtain Account Access Key.
-
Azure Storage Account Access Key: Enter the account access key you obtained in Step 3: Obtain Account Access Key.
-
Wildcard Log Schema: Provide the wildcard log schema.
-
-
(Optional) Next to the Basic Configuration section, click on the Advanced Options link to provide additional information about the event log data:
-
Enter one or more parameters that provide additional context about the data. For example, "File format" indicates the format of the event log data being shipped, or "File extension" that indicates the extension of the logs.
-
Enter the corresponding value of the parameter. For example, CSV is a file format. Similarly, ".gzip" is a file extension.
-
-
Click Save to add the log source.
Step 5: Configure permissions
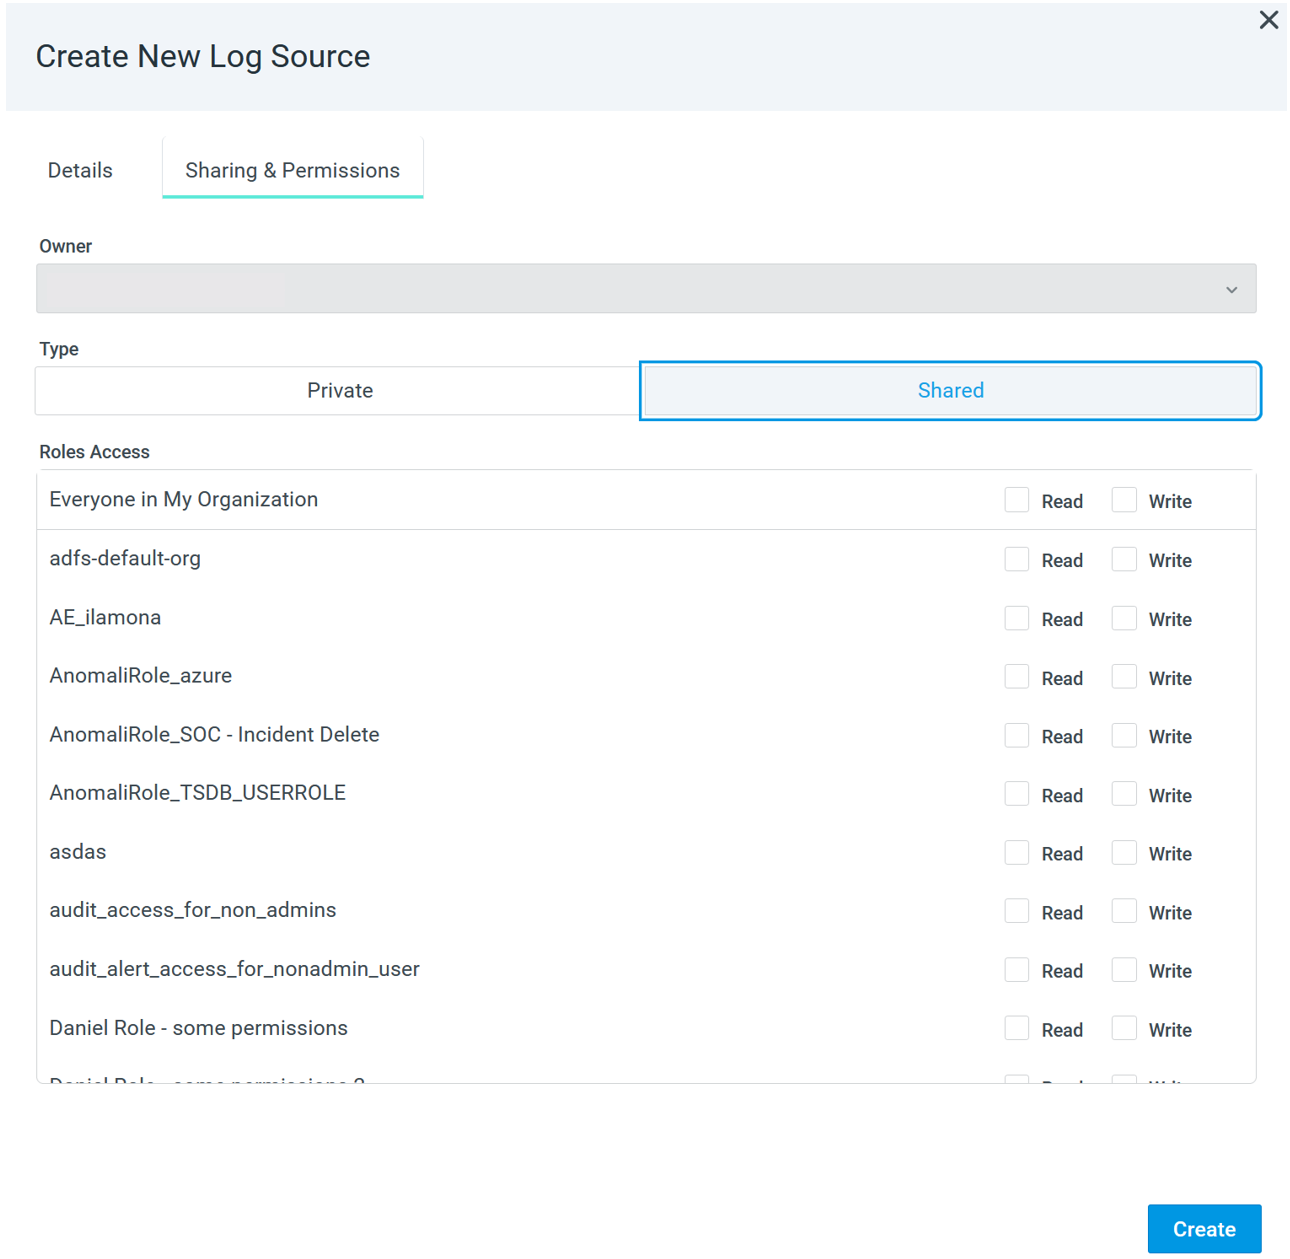
You can set permissions to decide which roles can view, add, or edit log sources. To do so, configure the following parameters:
-
Owner: Select an owner of the view from the list of users. This is the email address of the owner.
-
Type: Select the type of permission assigned to the view:
-
Private: Only the owner has read and write privileges, that is, no other user can access or edit the view.
-
Shared: Allows you to set the read-write privileges for a role that is mapped to different users, granting read-write permissions to all users assigned that role. You can also assign read or write permissions to everyone in your organization.
-
Step 6: Check log source status
Once added, the status of the log source becomes Create Requested. See Log Source Statuses to understand the different types statuses assigned to log sources.
Step 7: Receive confirmation email
You will receive a notification email from Anomali once you have created a new log source request. The Log Source Management page will show the status as Create Requested.
Once the log source has been provisioned and is ready for use, Anomali will send you another email and the Log Source Management page status for the log source will change to Active.