Microsoft Azure Active Directory
Anomali supports the ingestion of Microsoft Azure Active Directory (AD) logs either through Azure Storage account or AWS S3.
Azure Storage account
Prerequisites
-
Your organization must have an active subscription to Azure.
-
Your organization must have a Microsoft 365 E5 license. Refer to the Microsoft website for details.
-
You must deploy Microsoft Endpoint Defender to the hosts you intend to manage. See Microsoft's guide to Onboard devices and configure Microsoft Defender for Endpoint capabilities for details.
Step 1: Set Up Azure Resources
Complete Microsoft Azure workflows for the following activities to set up your Azure environment.
-
Create an Azure function based on the Azure Event Grid trigger template. See Microsoft's guide to Create Azure Function for details.
Under Code + Test, paste the following
event_sender.jscode provided by Anomali for this integration. Replace<username>:<apikey>with the username and API key for the ThreatStream user account you have provisioned to be a service account for this integration (refer to Prerequisites).const https = require('https'); module.exports = async function (context, eventGridEvent) { const eventData = JSON.stringify(eventGridEvent); const options = { hostname: 'api.threatstream.com', port: 443, path: '/api/v1/xdr/cloud_logsource/azure_storage/event/', method: 'POST', headers: { 'Content-Type': 'application/json', 'Content-Length': eventData.length, 'Authorization': 'apikey <username>:<apikey>' } }; const req = https.request(options, (res) => { console.log('statusCode:', res.statusCode); console.log('headers:', res.headers); res.on('data', (d) => { process.stdout.write(d); }); }); req.on('error', (e) => { console.error(e); }); req.write(eventData); req.end(); }; -
Provision an Azure Storage account for this integration.
-
Create an Azure Storage account. See Microsoft's guide to Create a storage account for more details.
-
After the Storage account has been created, add an Event Subscription to the Storage account configuration:
-
Go to Events and click + Event Subscription.
-
Select Event Grid Schema.
-
Under Filter to Event Types, select Blob Created.
-
Under Endpoint Type, select Azure Function.
-
For Endpoint, select the Azure function created for this integration in the previous step. See Microsoft's guide to Subscribe to custom topic for details.
-
-
Copy the Storage account name and Storage account access key to a safe place that you can access when you complete the Security Analytics log source configuration.
-
See Microsoft's guide on how to View account access keys for more details.
Step 2: Configure Endpoints to Stream Events to Azure Storage
Enable the Microsoft Defender Streaming API so managed hosts can stream event logs to Azure Storage.
-
Log in to Microsoft 365 Defender as a global admin or security admin.
-
Go to Settings > Microsoft 365 Defender > Streaming API.
-
Click Add.
-
In the Add new Streaming API settings, specify the Azure Storage account information set up in Step 1: Set Up Azure Resources.
-
Select only the following events: AlertEvidence, AlertInfo, DeviceNetworkEvents, DeviceProcessEvents, DeviceFileEvents, DeviceLogonEvents, DeviceFileCertificateInfo, DeviceImageLoadEvents, EmailEvents, EmailAttachmentInfo, EmailUrlInfo.
After you have deployed the required Microsoft components, Windows Defender will start capturing the events from the on-boarded devices.
Step 3: Add Azure Active Directory as new log source
To add Defender as a new log source on the Anomali platform:
-
Navigate to Search > Log Source Management.
-
Click New to add a new log source.
-
Enter a name for the log source.
-
(Optional) Enter a description for the log source.
-
Select Azure Active Directory as the source type.
-
Select API as the ingestion method.
-
Select API as the ingest method.
-
Provide the Basic Configuration details:
-
Azure Storage Account Name: Type the provisioned storage account name from Step 1: Set Up Azure Resources.
-
Azure Storage Account Access Key: Paste the key for the provisioned account from Step 1: Set Up Azure Resources.
-
Wildcard Log Schema: Provide the wildcard log schema.
-
(Optional) Raw events: Select Enable to collect and store the entire event log that is available from the log source.
-
-
(Optional) Next to the Basic Configuration section, click on the Advanced Options link to provide additional information about the event log data:
-
Enter one or more parameters that provide additional context about the data. For example, "File format" indicates the format of the event log data being shipped, or "File extension" that indicates the extension of the logs.
-
Enter the corresponding value of the parameter. For example, CSV is a file format. Similarly, ".gzip" is a file extension.
-
-
Click Save to add the log source.
Step 4: Configure permissions
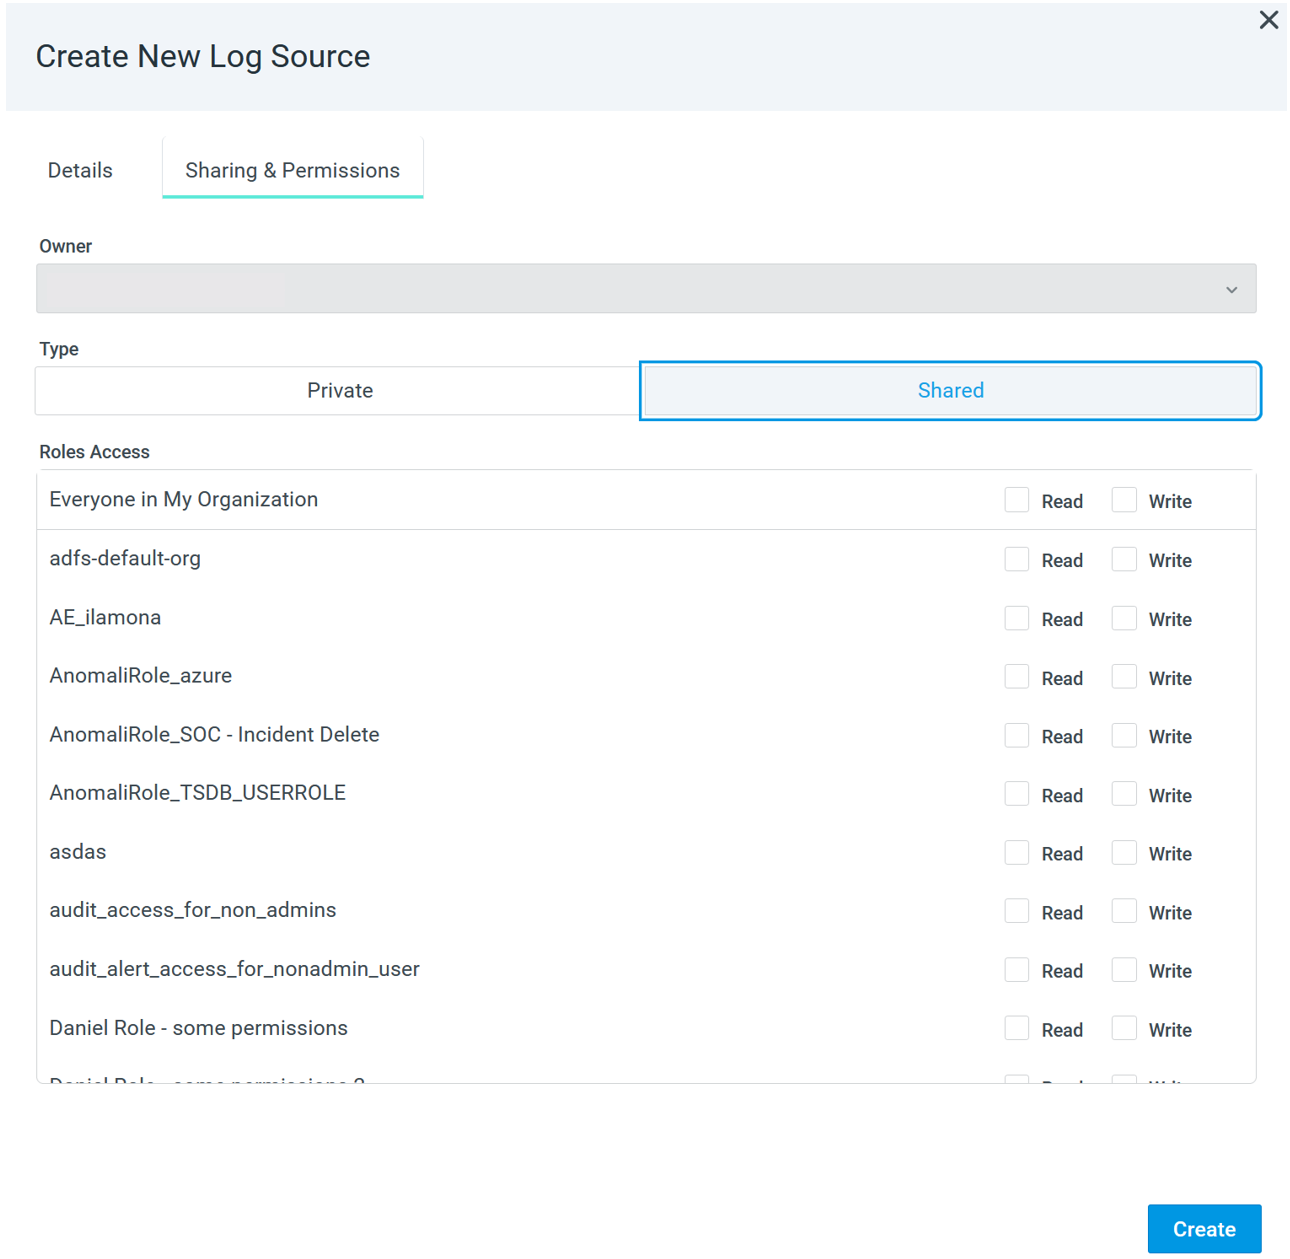
You can set permissions to decide which roles can view, add, or edit log sources. To do so, configure the following parameters:
-
Owner: Select an owner of the view from the list of users. This is the email address of the owner.
-
Type: Select the type of permission assigned to the view:
-
Private: Only the owner has read and write privileges, that is, no other user can access or edit the view.
-
Shared: Allows you to set the read-write privileges for a role that is mapped to different users, granting read-write permissions to all users assigned that role. You can also assign read or write permissions to everyone in your organization.
-
Step 5: Check log source status
Once added, the status of the log source becomes Create Requested. See Log Source Statuses to understand the different types statuses assigned to log sources.
Step 6: Receive confirmation email
You will receive a notification email from Anomali once you have created a new log source request. The Log Source Management page will show the status as Create Requested.
Once the log source has been provisioned and is ready for use, Anomali will send you another email and the Log Source Management page status for the log source will change to Active.
AWS S3
If your logs are already in S3, you can proceed directly to Step 2: Set up SQS queue. If not, Anomali recommends following Step 1: Ship data to S3 using NXLog to use NXLog to first ship the logs to S3. After S3 receives the data, it sends updates to an Amazon SQS queue you designate, enabling Anomali to automatically pull the logs from S3 whenever it receives a new notification from the queue.
Onboarding Steps
Step 1: Ship data to S3 using NXLog
See Using NXLog to Ship Data to set up NXLog to send data into S3.
Step 2: Set up SQS queue
Once your data is in S3, you can send it to Anomali using Amazon SQS. See Setting up Amazon SQS queue for more information.
Step 3: Enable AWS S3 notifications
Enable AWS S3 notifications for Amazon SQS to receive change notifications when you add logs. See Amazon's guide to configuring AWS S3 notification for SQS for more information.
Step 4: Add Azure Active Directory as new log source
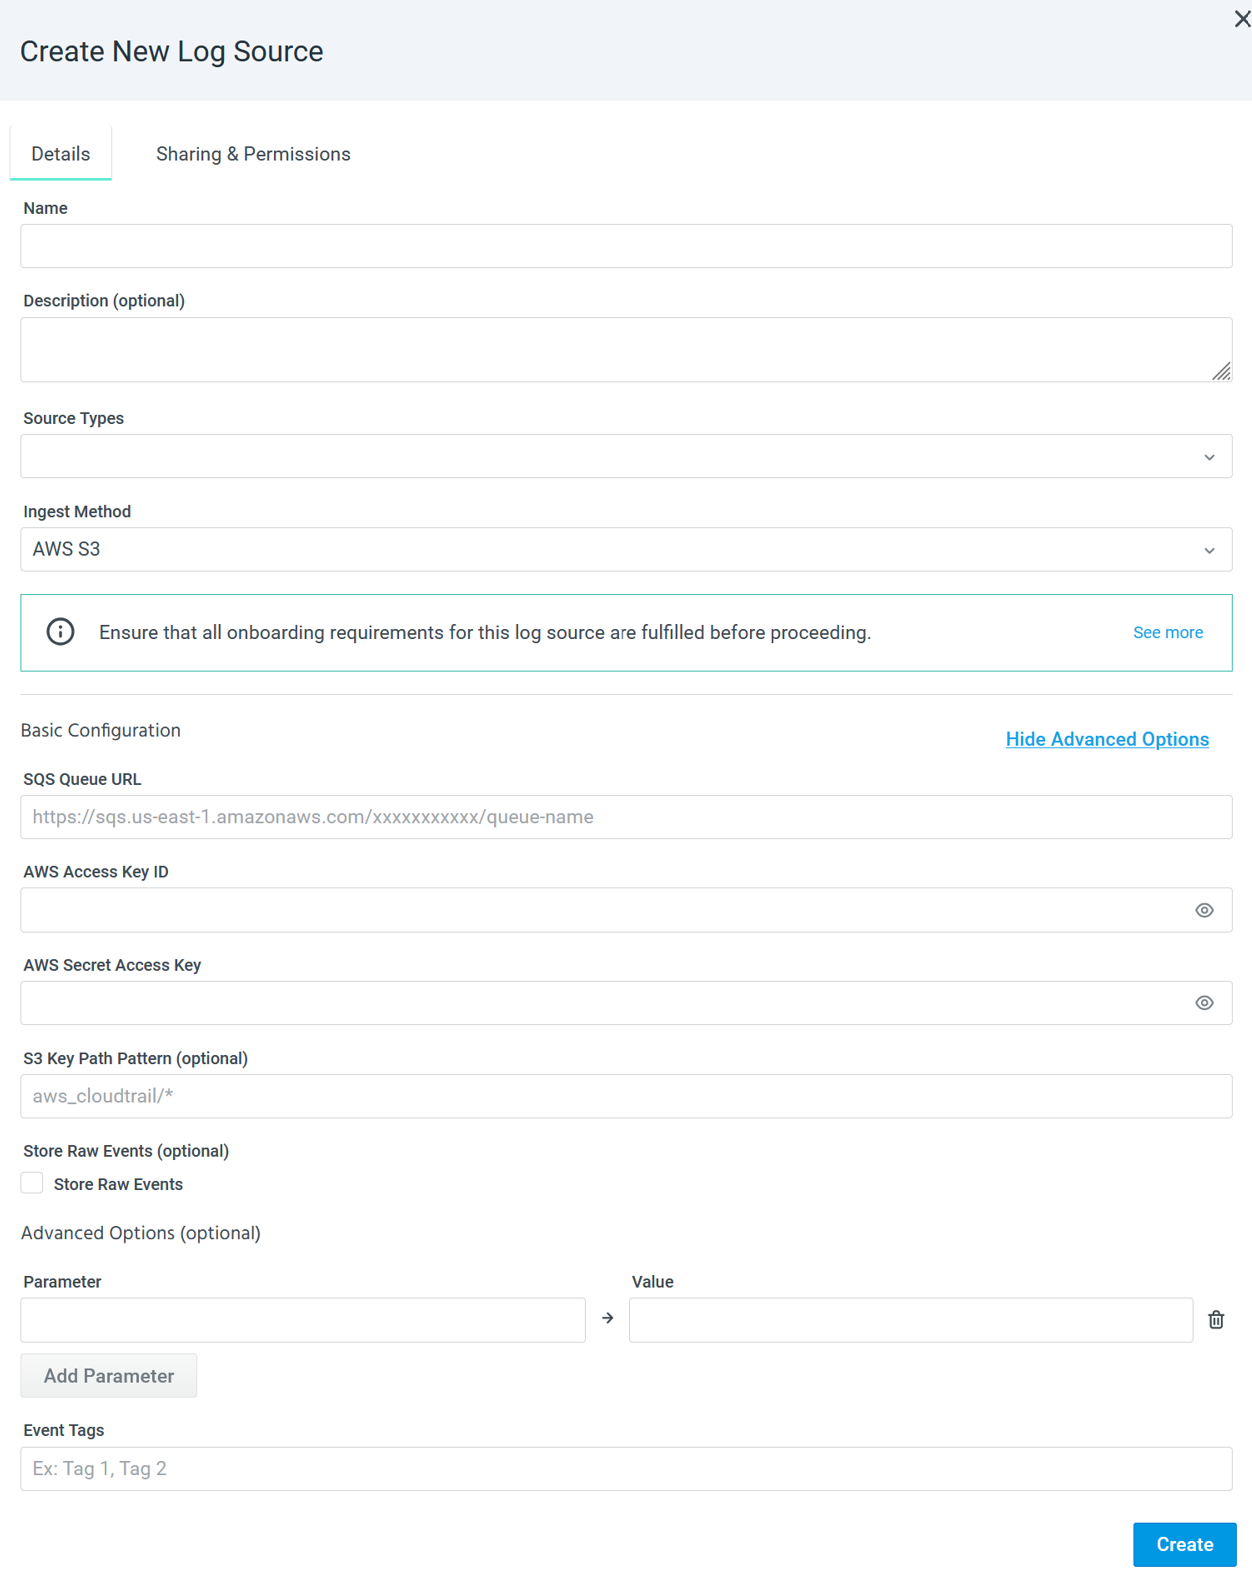
On the Anomali platform, add Azure Active Directory as a new log source, as follows:
-
Navigate to Search > Log Source Management.
-
Click New to add a new log source.
-
Enter a name for the log source.
-
(Optional) Enter a description for the log source.
-
Select it as the log source.
-
Select AWS S3 as the ingest method.
-
Ensure S3 notification are enabled. See Step 2: Enable AWS S3 notifications for more information.
-
Provide the Basic Configuration details:
-
AWS SQS Queue URL: Enter the URL of your AWS SQS queue. See Setting up Amazon SQS queue for more information.
-
AWS Secret Access Key: Provide the AWS secret access key.
-
AWS Access Key ID: Enter the AWS Access ID.
-
File Selector: Provide the path to the event log data files. Anomali recommends the following practices for the path:
-
-
Sourcetype must be the path prefix, as follows:
<sourcetype>/year=2025/month=04/day=05/path/to/file.
For example:azure_active_directory/year=2025/month=03/day=22/events/event_data_logs/. -
Sourcetype name must not contain any spaces: For example,
"azure_active_directory"is correct, however"azure_active_directory"is incorrect.
-
(Optional) Next to the Basic Configuration section, click on the Advanced Options link to provide additional information about the event log data:
- Enter one or more parameters that provide additional context about the data. For example, "File format" indicates the format of the event log data being shipped, or "File extension" that indicates the extension of the logs.
- Enter the corresponding value of the parameter. For example, CSV is a file format. Similarly, ".gzip" is a file extension.
-
Click Save to add the log source.
Step 5: Configure permissions
You can set permissions to decide which roles can view, add, or edit log sources. To do so, configure the following parameters:
-
Owner: Select an owner of the view from the list of users. This is the email address of the owner.
-
Type: Select the type of permission assigned to the view:
-
Private: Only the owner has read and write privileges, that is, no other user can access or edit the view.
-
Shared: Allows you to set the read-write privileges for a role that is mapped to different users, granting read-write permissions to all users assigned that role. You can also assign read or write permissions to everyone in your organization.
-
Step 6: Check log source status
Once added, the status of the log source becomes Create Requested. See Log Source Statuses to understand the different types statuses assigned to log sources.
Step 7: Receive confirmation email
You will receive a notification email from Anomali once you have created a new log source request. The Log Source Management page will show the status as Create Requested.
Once the log source has been provisioned and is ready for use, Anomali will send you another email and the Log Source Management page status for the log source will change to Active.