About the Heatmap Visualization Type
Use the Heatmap visualization type to quickly identify patterns, trends, and anomalies by displaying the data in a form of a matrix, where values are represented by varying colors.
(Click the image to enlarge it.)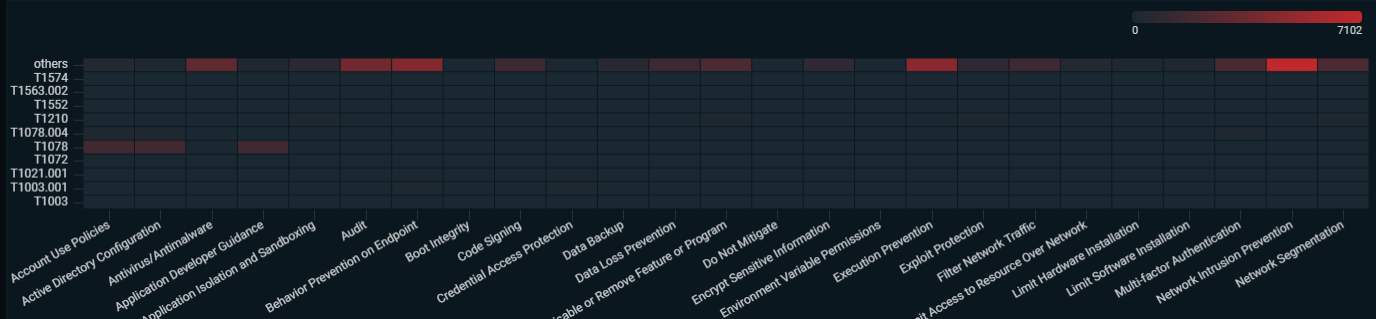
You can use heatmaps to:
-
Plot the volume of traffic between different IP addresses over time. This can help you spot potential DDoS attacks or unusual data exfiltration.
-
Show the number of failed login attempts across different user accounts and time periods and, as a result, highlight hotspots of suspicious activity.
-
Plot the volume and types of user activities across different departments or roles in order to identify unusual behavior and therefore, detect insider threats or policy violations.
AQL Expression Requirements
The heatmap visualization type is used to show counts. The query must have the following elements to return the required data:
-
A result set in a form of a matrix with numeric values.
-
Use the
aggroperator, which returns a numeric value.
The following is an example of a query that returns the required data:
techniques
| where name in ($name)
| fields system_requirements as mitigation, technique
| chart count as cnt by mitigation,technique
Note: Using addtotals=true in your timechart operator query appends a total row and total column to your results. The total row shows the aggregate count per group across the entire time range, and the total column shows the aggregate count across all groups per time bucket. This is useful for comparing entities and spotting volume trends, without needing a separate query. See timechart operator for more information.
Panel Options
Use the options in the Panel tab to customize the options described in the following table.
| Setting | Description | |
|---|---|---|
| Settings | Panel title | Titles appear at the top of a panel. |
| Description | Descriptions appear as tooltips. Markdown and links are supported. | |
| Transparent | Display panel without a background. | |
| Display | Scheme |
Select a color scheme. |
| Rotate x-axis tick labels | Specify the angle with which the labels will be rotated for better label readability. |
Field Options
Use the options in the Fields tab to customize the options described in the following table.
| Setting | Description | |
|---|---|---|
| Data links | Add link |
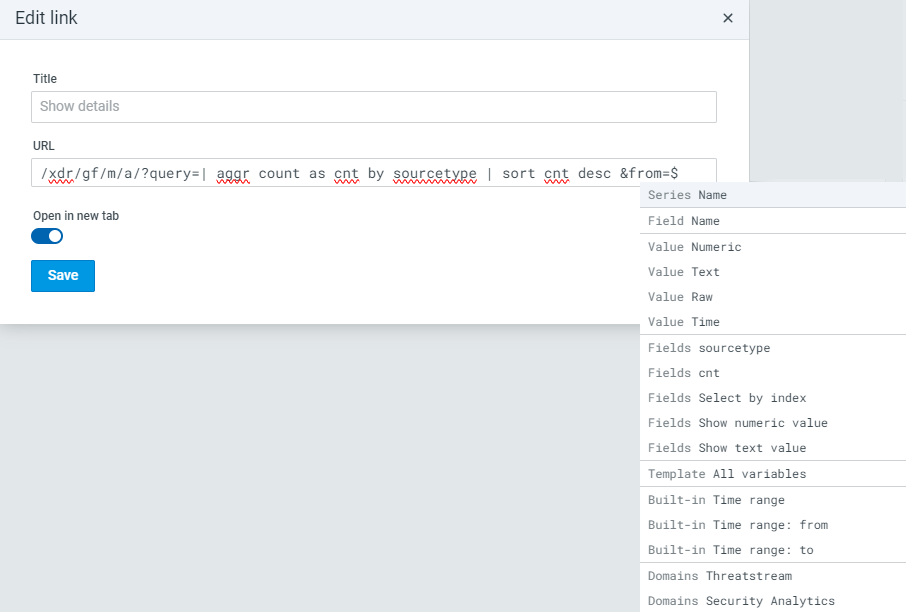
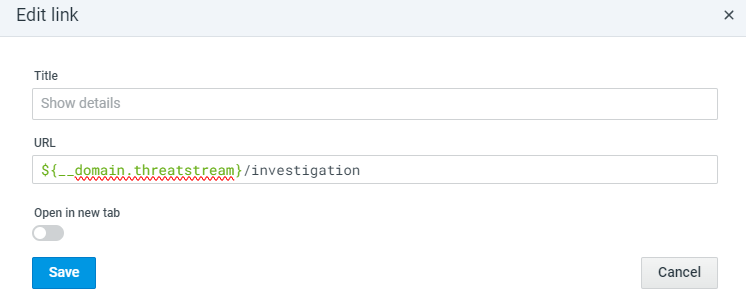
Click +Add link and complete settings for link behavior when a user clicks data fields in the visualization. You can use the following URL types and configure them to pass variables:
To use a relative URL, specify
To use a URL in ThreatStream or Security Analytics domains, do the following:
|
Advanced Options
Use the options in the Advanced tab to override the settings configured in the Fields tab for particular fields. For example, you can override the automatic color palette selected for a particular field to a preferred single color.
You have the following options to select field settings to be overridden:
-
Fields with name: Set properties for a specific field.
-
Fields with name matching regex: Set properties for fields with names matching a regex.
-
Fields with type: Set properties for fields with a specific type (numeric, string, Boolean).
-
Fields returned by query: Set properties for fields from a specific query.