Mimecast 1.0
Anomali supports the ingestion of Mimecast logs through the Mimecast API 1.0 and AWS S3.
API 1.0 call
You can use your existing Mimecast Access and Secret Keys or create them to add a new log source in the Anomali platform.
Onboarding steps
Prerequisites
-
Admin access to the Mimecast admin console.
-
The admin must be assigned a role with read and edit API app permissions.
-
Security permissions must permit the management of app roles.
Step 1: Retrieve custom App ID and App Key
To create a custom API app, see the Mimecast guide to Creating an API 2.0 application and follow the Version 1.0 Integration flow instead.
After creating the app, see the Mimecast console to retrieve the App ID and App Key. Securely store these details for the next steps.
Step 2: Create new user
You must create a user profile with the correct permissions to generate API keys for Mimecast collector authentication. To create a user:
-
Sign into the admin console.
-
Navigate to the Administration > Directories > Internal Directories to view a list of internal domains.
-
Click the internal domain where you would like to create your new user.
-
Click New Address and complete the form to create a new user.
-
Keep a note of the email address and password. You will use them in Step 7: Create Access and Secret Keys.
Step 3: Add user to admin role
-
Navigate to Administration > Account > Roles.
-
Right-click the Basic Administrator role and click Add users to role.
-
Select the new user you created.
-
Click Add selected users.
Step 4: Create new user group
-
Navigate to Administration > Directories > Profile Groups menu.
-
Click the + icon on the parent folder where you would like to create the group. This creates a new group with the name New Folder.
-
If you prefer renaming, click the group and use the text box to change the name.
-
Navigate to Build > Add Email Addresses and enter the email address of the new user you created.
-
Click Save and Exit.
Step 5: Create new authentication profile
-
Navigate to Administration > Services > Applications menu.
-
Click Authentication Profiles > New Authentication Profile.
-
Enter a description for the new profile.
-
Set the Authentication TTL setting to Never Expires. This ensures that your token does not expire, avoiding restrictive data collection.
-
Leave other settings as default.
-
Click Save and Exit.
Step 6: Create new app setting
-
Navigate to Administration > Services > Applications menu.
-
Click New Application Settings > New Authentication Profile to enter a description.
-
In the Group field, paste the group you created.
-
In the Authentication Profile field, select the authentication profile you created.
-
Click Save and Exit.
Step 7: Create Access and Secret Keys
-
Navigate to Administration > Services > API and Platform Integrations menu.
-
Navigate to the Your Application Integrations tab.
-
Click the application you created, then Create Keys.
-
Enter the email address of the service account created in Step 2, then click Next.
-
In the Authentication dialog popup, enter:
-
Type: Cloud
-
Password: Enter the user profile password you created.
-
-
Click Next.
-
If prompted, complete the multi-factor authentication.
-
Click Next.
-
Securely save the Access Key and Secret Key for Step 8: Add Mimecast as new log source.
Step 8: Add Mimecast as new log source
To add Mimecast as a new log source on the Anomali platform:
-
Navigate to Search > Log Source Management.
-
Click New to add a new log source.
-
Enter a name for the log source.
-
(Optional) Enter a description for the log source.
-
Select Mimecast as the source type.
-
Select API as the ingestion method.
-
Select API as the ingest method.
-
Provide the Basic Configuration details:
-
App ID: Enter the application ID to authenticate requests.
-
App Key: Enter the app key to authenticate requests.
-
Access Key: Enter the access key to authenticate requests.
-
Secret Key: Enter the secret key to authenticate requests.
-
Admin Email Address: Email address for the service account provisioned for this integration.
-
Important: The email address you specify here must be the email address associated with the service account access key provisioned for this integration.
-
-
(Optional) TTP Attachment Logs: Select whether to collect these TTP attachment logs. Enabled by default.
-
(Optional) TTP URL Logs: Select whether to collect these TTP URL logs. Enabled by default.
-
(Optional) TTP Impersonation Logs: Select whether to collect these TTP impersonation logs. Enabled by default.
-
(Optional) Threat Intel Feed: Select whether to collect these threat intel feed logs. Enabled by default.
-
(Optional) Ingestion Interval: Specify a number of minutes, hours, or days between API requests.
-
-
(Optional) Next to the Basic Configuration section, click on the Advanced Options link to provide additional information about the event log data:
-
Enter one or more parameters that provide additional context about the data. For example, "File format" indicates the format of the event log data being shipped, or "File extension" that indicates the extension of the logs.
-
Enter the corresponding value of the parameter. For example, CSV is a file format. Similarly, ".gzip" is a file extension.
-
-
Click Save to add the log source.
Step 9: Configure permissions
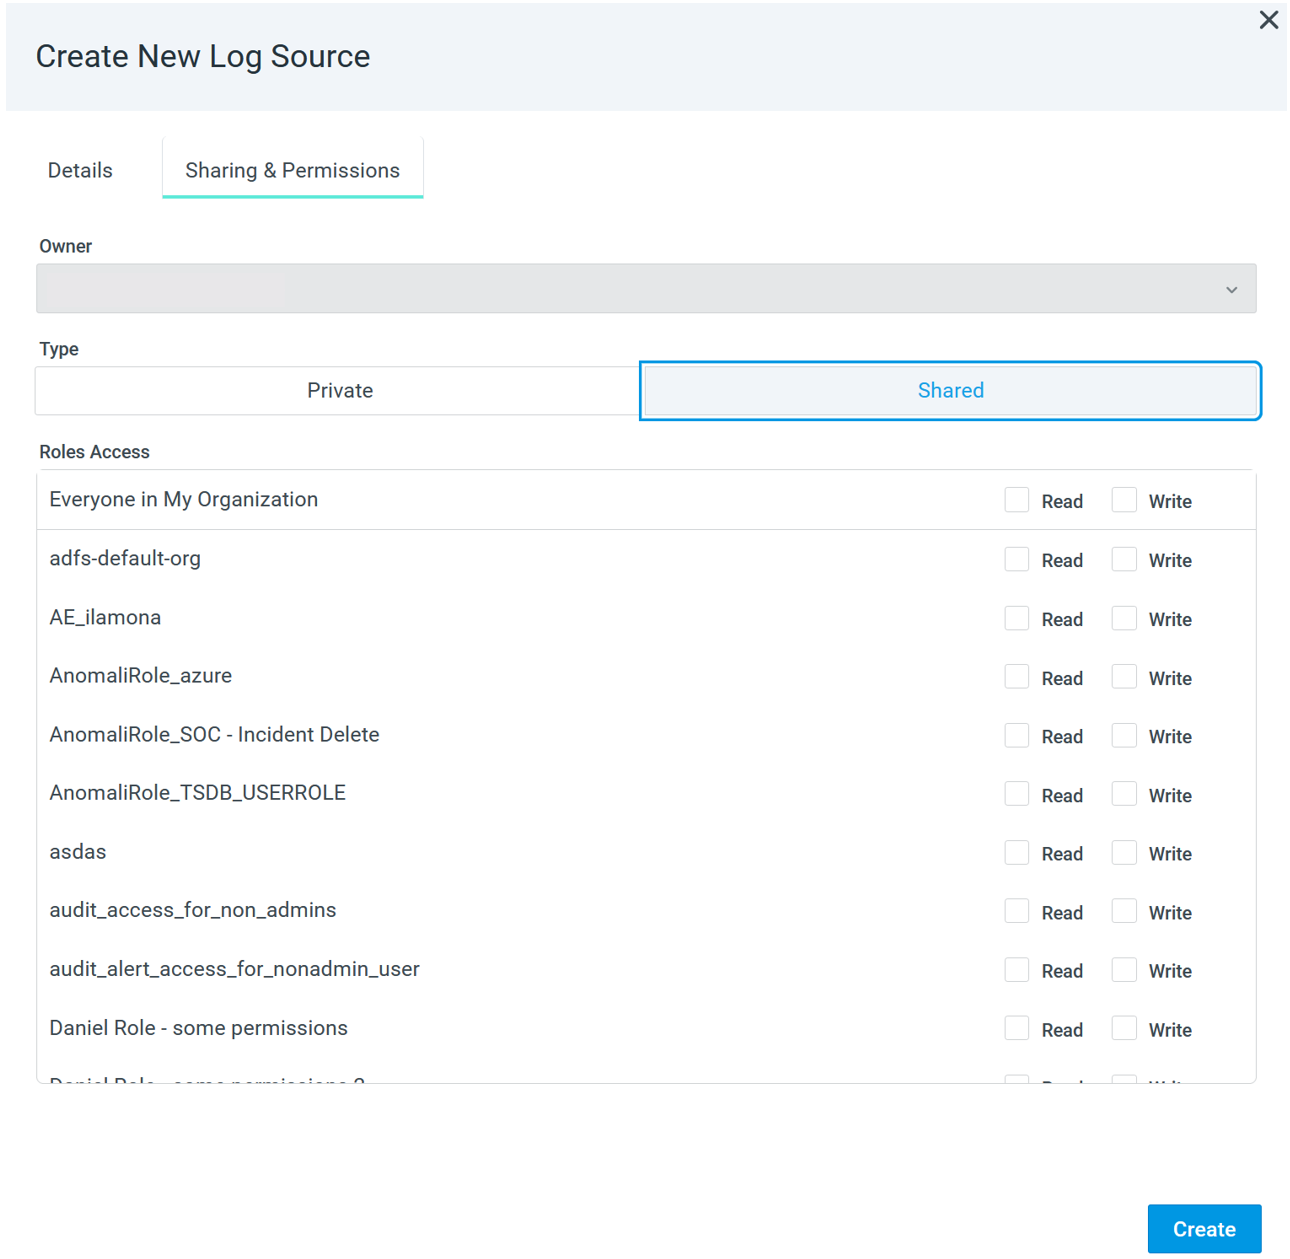
You can set permissions to decide which roles can view, add, or edit log sources. To do so, configure the following parameters:
-
Owner: Select an owner of the view from the list of users. This is the email address of the owner.
-
Type: Select the type of permission assigned to the view:
-
Private: Only the owner has read and write privileges, that is, no other user can access or edit the view.
-
Shared: Allows you to set the read-write privileges for a role that is mapped to different users, granting read-write permissions to all users assigned that role. You can also assign read or write permissions to everyone in your organization.
-
Step 10: Check log source status
Once added, the status of the log source becomes Create Requested. See Log Source Statuses to understand the different types statuses assigned to log sources.
Step 11: Receive confirmation email
You will receive a notification email from Anomali once you have created a new log source request. The Log Source Management page will show the status as Create Requested.
Once the log source has been provisioned and is ready for use, Anomali will send you another email and the Log Source Management page status for the log source will change to Active.
AWS S3
If your logs are already in S3, you can proceed directly to Step 2: Create new user. If not, Anomali recommends following Step 1: Ship data to S3 using NXLog to use NXLog to first ship the logs to S3. After S3 receives the data, it sends updates to an Amazon SQS queue you designate, enabling Anomali to automatically pull the logs from S3 whenever it receives a new notification from the queue.
Onboarding Steps
Step 1: Ship data to S3 using NXLog
See Using NXLog to Ship Data to set up NXLog to send data into S3.
Step 2: Set up SQS queue
Once your data is in S3, you can send it to Anomali using Amazon SQS. See Setting up Amazon SQS queue for more information.
Step 3: Enable AWS S3 notifications
Enable AWS S3 notifications for Amazon SQS to receive change notifications when you add logs. See Amazon's guide to configuring AWS S3 notification for SQS for more information.
Step 4: Add Mimecast as new log source
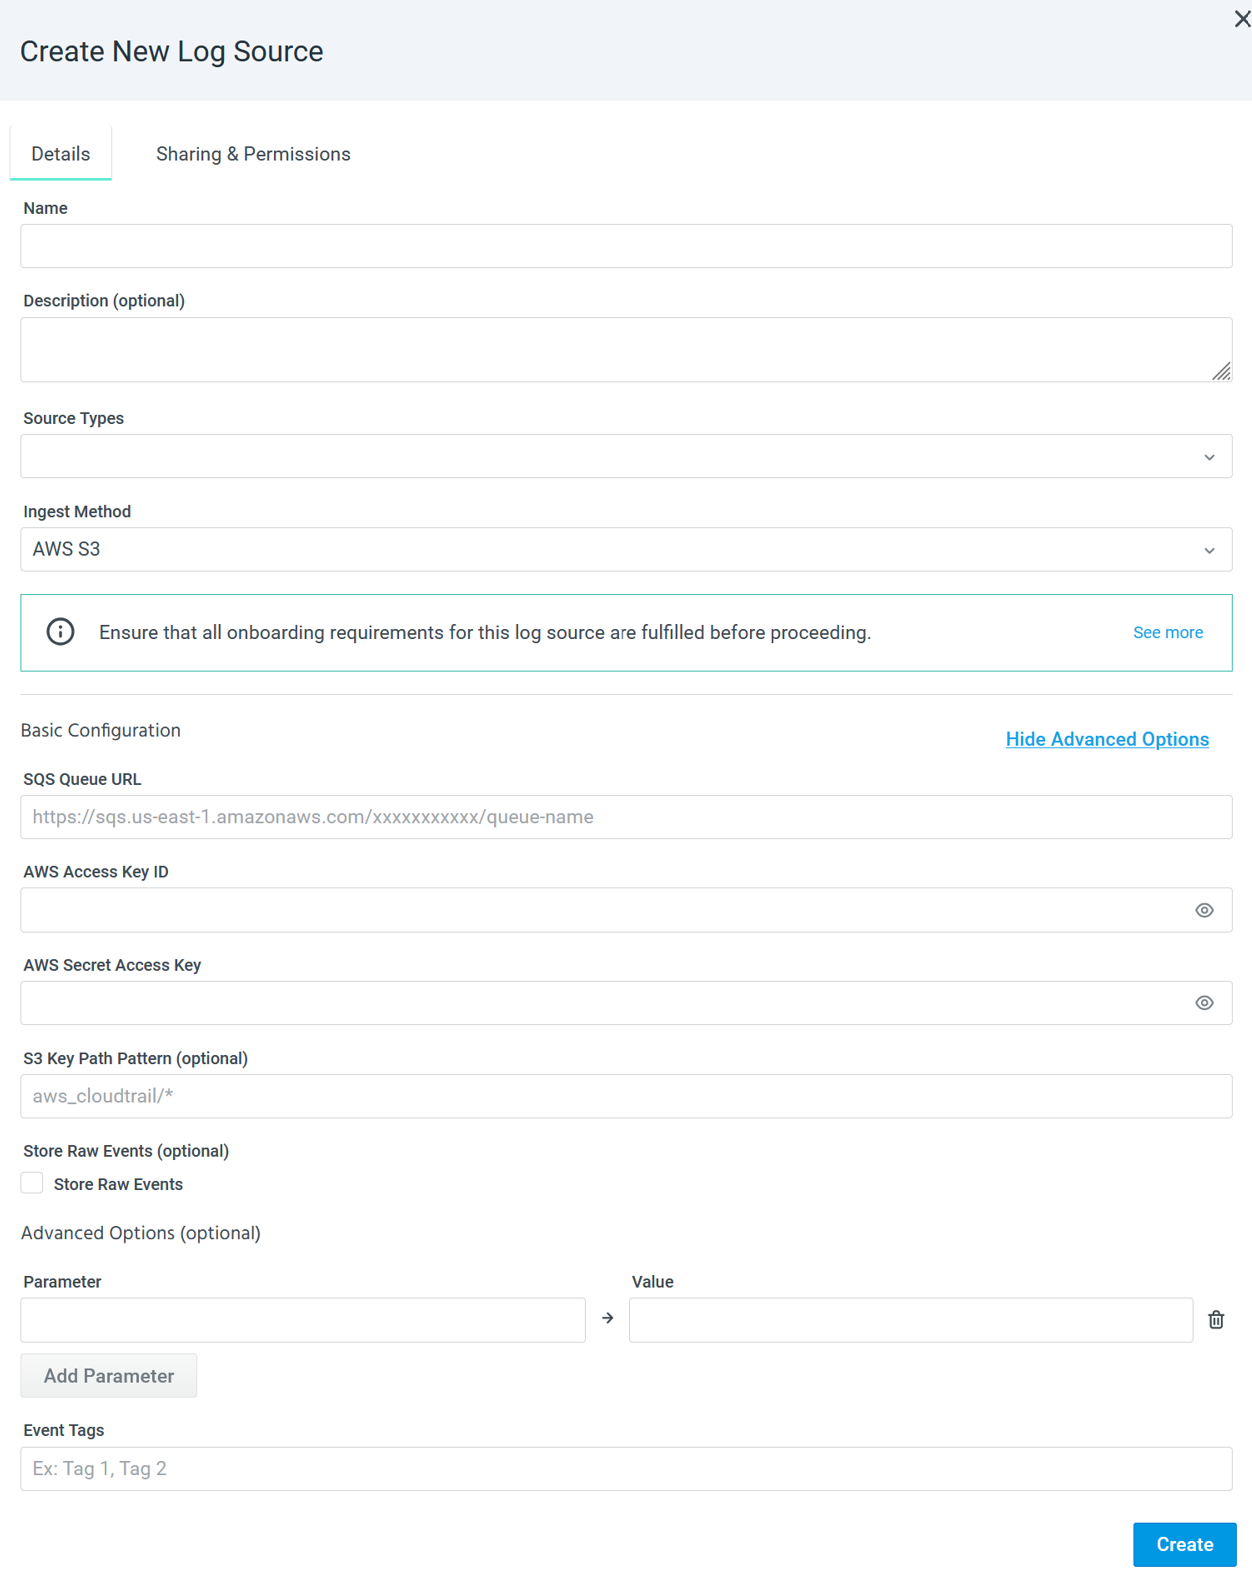
On the Anomali platform, add Mimecast as a new log source, as follows:
-
Navigate to Search > Log Source Management.
-
Click New to add a new log source.
-
Enter a name for the log source.
-
(Optional) Enter a description for the log source.
-
Select it as the log source.
-
Select AWS S3 as the ingest method.
-
Ensure S3 notification are enabled. See Step 2: Enable AWS S3 notifications for more information.
-
Provide the Basic Configuration details:
-
AWS SQS Queue URL: Enter the URL of your AWS SQS queue. See Setting up Amazon SQS queue for more information.
-
AWS Secret Access Key: Provide the AWS secret access key.
-
AWS Access Key ID: Enter the AWS Access ID.
-
File Selector: Provide the path to the event log data files. Anomali recommends the following practices for the path:
-
-
Sourcetype must be the path prefix, as follows:
<sourcetype>/year=2025/month=04/day=05/path/to/file.
For example:mimecast/year=2025/month=03/day=22/events/event_data_logs/. -
Sourcetype name must not contain any spaces: For example,
"mimecast"or"mimecast_sourcetype"are correct, however"mimecast sourcetype"is incorrect.
-
(Optional) Next to the Basic Configuration section, click on the Advanced Options link to provide additional information about the event log data:
- Enter one or more parameters that provide additional context about the data. For example, "File format" indicates the format of the event log data being shipped, or "File extension" that indicates the extension of the logs.
- Enter the corresponding value of the parameter. For example, CSV is a file format. Similarly, ".gzip" is a file extension.
-
Click Save to add the log source.
Step 5: Configure permissions
You can set permissions to decide which roles can view, add, or edit log sources. To do so, configure the following parameters:
-
Owner: Select an owner of the view from the list of users. This is the email address of the owner.
-
Type: Select the type of permission assigned to the view:
-
Private: Only the owner has read and write privileges, that is, no other user can access or edit the view.
-
Shared: Allows you to set the read-write privileges for a role that is mapped to different users, granting read-write permissions to all users assigned that role. You can also assign read or write permissions to everyone in your organization.
-
Step 6: Check log source status
Once added, the status of the log source becomes Create Requested. See Log Source Statuses to understand the different types statuses assigned to log sources.
Step 7: Receive confirmation email
You will receive a notification email from Anomali once you have created a new log source request. The Log Source Management page will show the status as Create Requested.
Once the log source has been provisioned and is ready for use, Anomali will send you another email and the Log Source Management page status for the log source will change to Active.