Managing Detection Rules
You can take several actions on detection rules to which you have access. You can edit the configuration of a rule, view its detection history to see firing trends and outcomes over time, or duplicate a rule to create an independent, editable copy. This is especially useful if you want to build a variant of an Anomali authored rule, since those cannot be edited directly. You can also test a rule against recent data to confirm its logic works as expected, without triggering real alerts or creating detection records. Additionally, you can manage access to your rules, disable them temporarily, and enable them again when you are ready to resume normal operation, either one at a time or in bulk. Finally, you can delete rules you no longer need.
Editing Detection Rules
Detection rules can be edited on the Detection Rules page or directly from a detection rule match on the Detections page.
Only Organization Administrators, and users who have both the Manage Detection Rules permission and write ACL on the specific rule, can edit it. Rule owners inherently have owner-level access, so as long as they also hold the Manage Detection Rules permission, they can edit rules they own. See Detection Rule Actions and Their Required Permissions for details.
Anomali authored detection rules cannot be edited.
Editing Detection Rules from the Detections Rules Page
To edit a detection rule:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
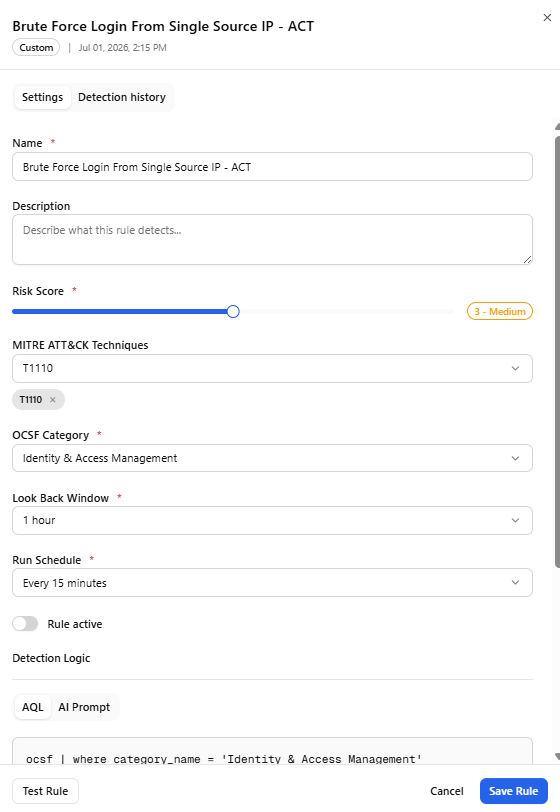
On the Detection Rules page, click the rule of your interest. Alternatively, open the more options menu (...) for the detection rule and then click Edit. The rule opens in the edit mode.
-
On the Settings tab, configure the fields you need.
-
Click Test Rule to confirm that your changes are valid.
-
Click Save Rule.
Editing Detection Rules from Detection Rule Matches
To edit a detection rule from a detection rule match:
-
Navigate to ThreatStream Next Gen > Security Operations > Detections.
-
On the Detections page, locate a detection rule match whose rule you want to update and click the corresponding more options menu (...).
-
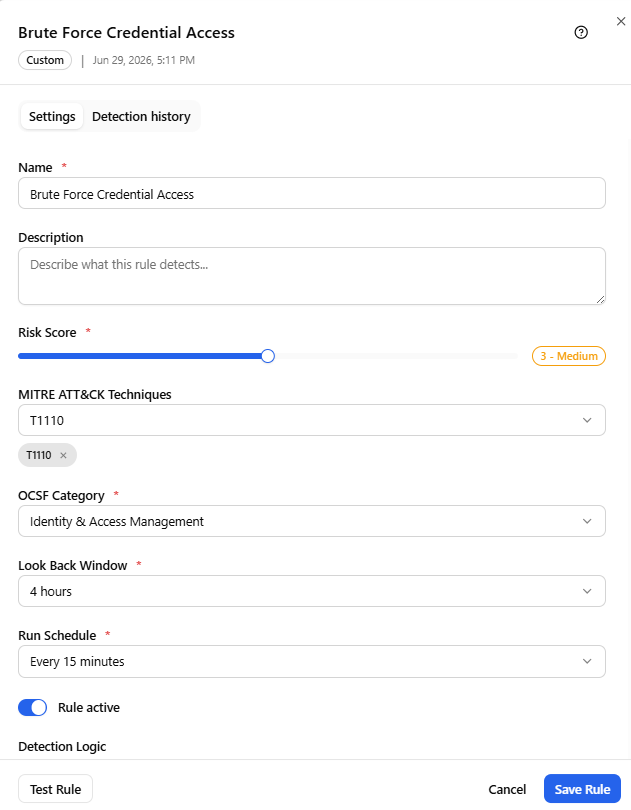
Click Edit Rule.
-
On the Settings tab, configure the fields you need.
-
Click Test Rule to confirm that your changes are valid.
-
Click Save Rule.
Viewing Detection History
Detection History is the activity log of a detection rule, showing both the trend (how often it has been firing over the last month) and the detail (each individual firing event and what happened to the detections it produced).
To view detection history of a rule:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
On the Detection Rules page, click the rule whose detection history you want to view. Alternatively, open the more options menu (...) for the detection rule and then click Edit.
-
Click Detection History.
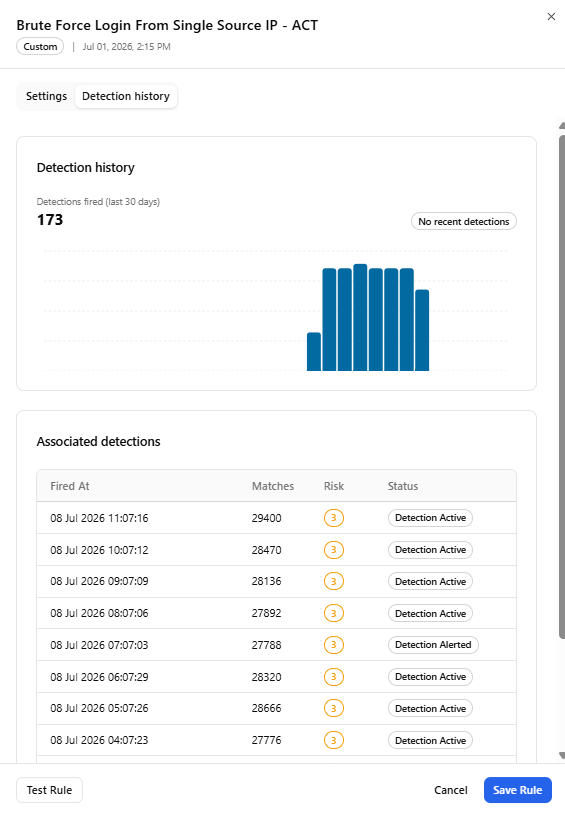
The Detection history chart displays a day-by-day chart of firing volume alongside a status indicator.
The Associated detections table shows a row for every time the rule has fired, listing the timestamp of when it was fired, the number of records matched in that run, the risk score assigned to that firing, and the resulting outcome, shown as either Detection Active or Detection Alerted.
-
Click Save Rule or Cancel when done.
Duplicating Detection Rules
Duplicating a detection rule gives you an independent, editable copy of the full configuration for an existing rule, so you can build on logic that already works instead of starting from scratch. You will find this especially useful when working with Anomali Authored rules, since you cannot edit those directly. See Detection Packs for details.
Duplicate an Anomali Authored rule, and you will get a custom variant you are free to tune however you like, while the original rule stays untouched. You might also reach for duplication when you want to create a variant of a rule with a different threshold or Look Back Window, test a change to the detection logic without risking the version already running in production, adapt the same logic to a different OCSF category or MITRE technique, or quickly build out a set of related rules that share most of the setup but differ in just one or two conditions.
To duplicate a detection rule:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
On the Detection Rules page, locate the detection rule of your interest.
-
Open the corresponding more options menu (...) and click Duplicate.
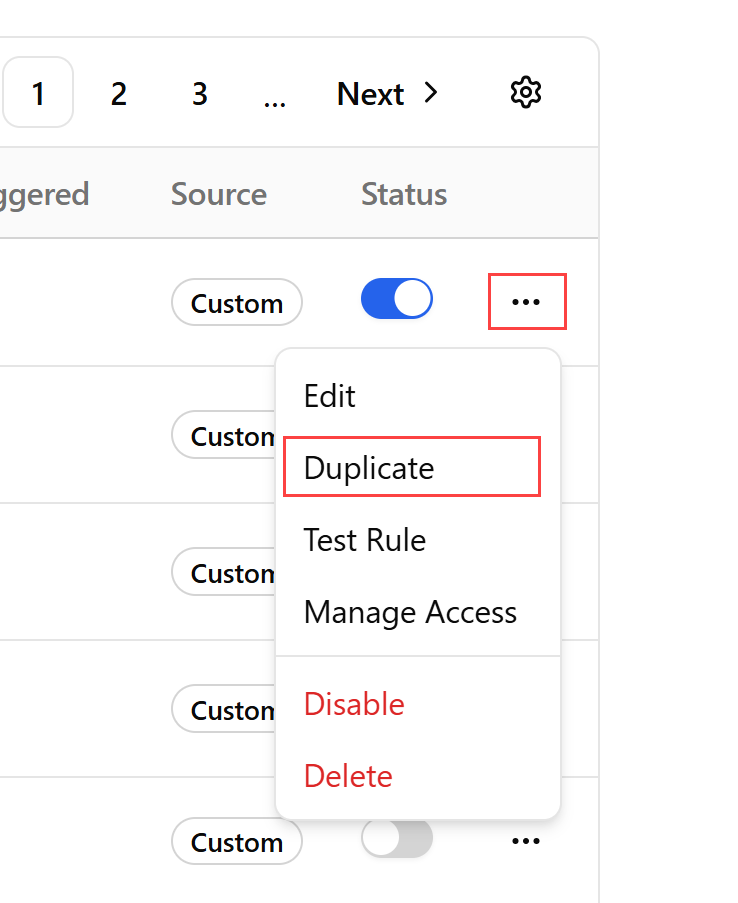
The rule duplicate is added to the list of detection rules with the word (Copy) appended to its original name.
Testing Detection Rules
Testing an already-created detection rule lets you confirm its logic still behaves as expected before making it active or after adjusting it, using real historical data with no risk of side effects. Since a test run does not create detection records or trigger any alerts, you can run it as many times as needed to check whether the rule finds what you intend.
To test a detection rule:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
On the Detection Rules page, locate the detection rule you want to test.
-
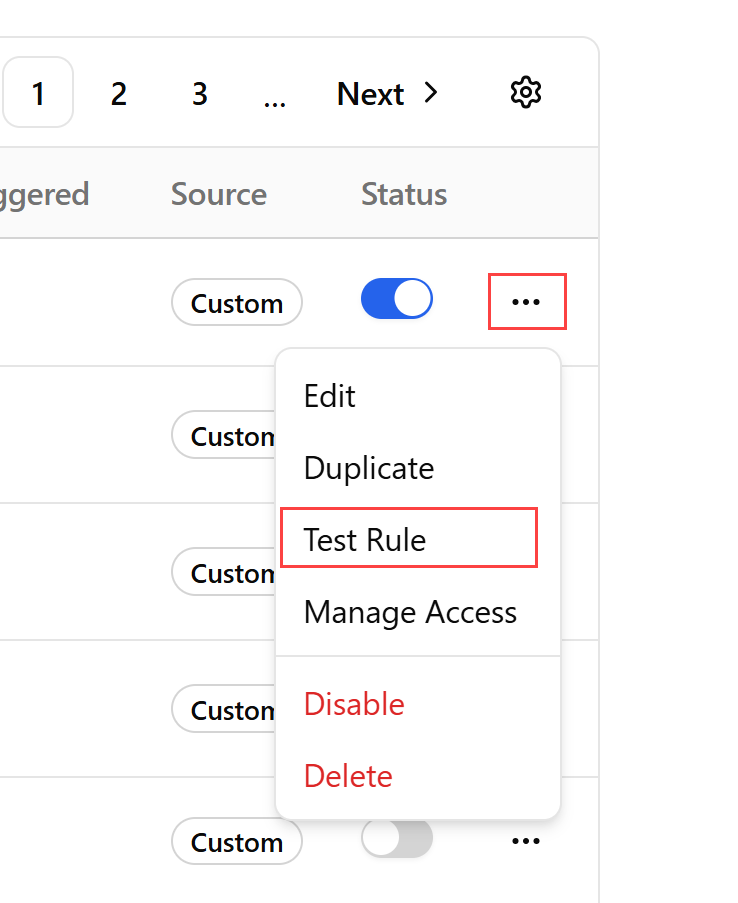
Open the corresponding more options menu (...) and click Test Rule.
-
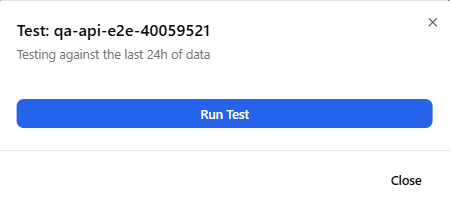
In the pop-up message that appears, click Run Test. The test is performed against the last 24 hours of data.
-
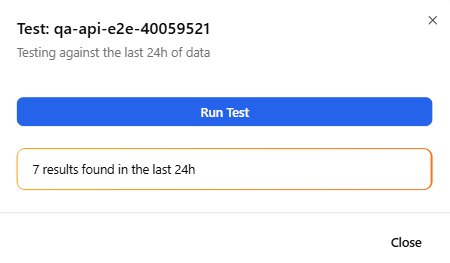
View test results.
Managing Access to Detection Rules
For details on managing access to detection rules, see Managing Access to Detection Rules.
Disabling Detection Rules
You can disable a Detection Rule to temporarily stop it from running without deleting it. Common reasons include tuning a rule that's generating too many false positives, working through a maintenance window where expected activity would otherwise trigger it, or keeping a superseded rule as a backup after replacing it with a newer one.
You can disable an individual detection rule or in bulk.
To disable a detection rule:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
On the Detection Rules page, locate the detection rule you want to disable.
-
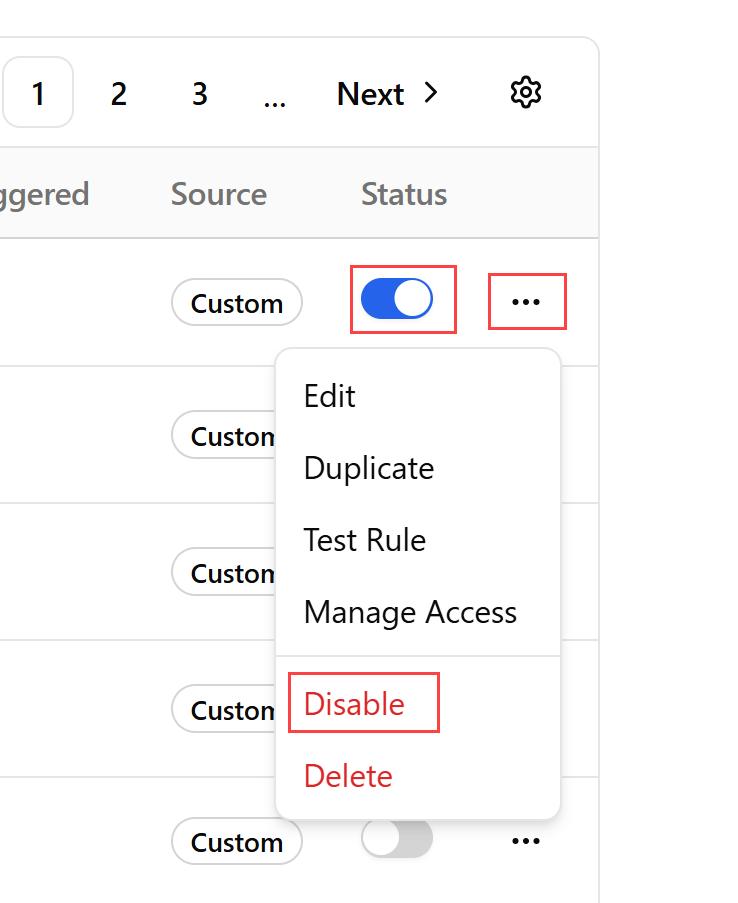
Click the corresponding toggle in the Status column.
Alternatively, open the corresponding more options menu (...) and click Disable.
-
In the pop-up message that appears, click Disable.
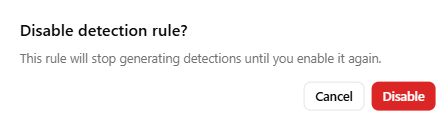
The detection rule is disabled.
To disable detection rules in bulk:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
On the Detection Rules page, select the detection rules you want to disable and click Disable Selected.
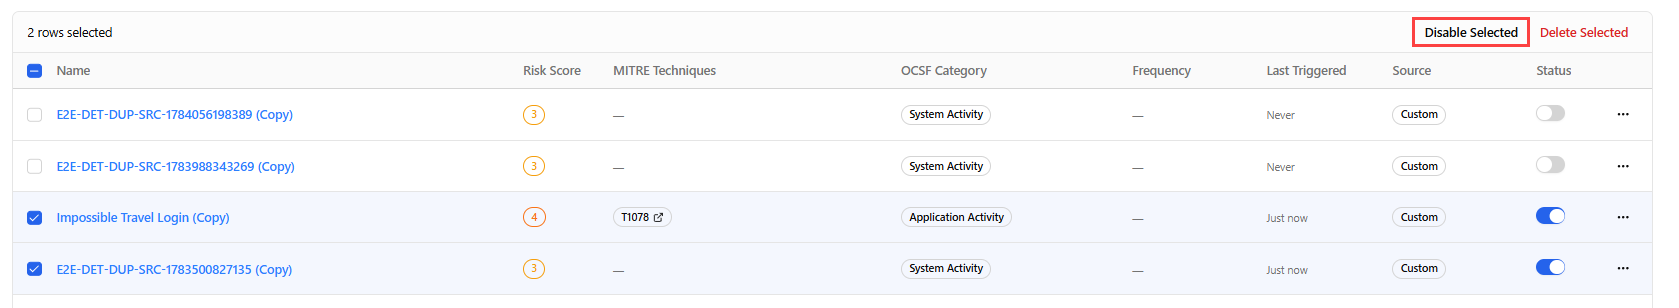
The selected detection rules are disabled.
Enabling Detection Rules
You can enable a detection rule to resume its scheduled execution after it has been disabled.
To enable a disabled detection rule:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
On the Detection Rules page, locate the detection rule you want to enable.
-
Click the corresponding toggle in the Status column.
Alternatively, open the corresponding more options menu (...) and click Enable.
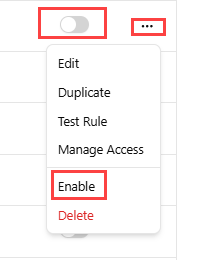
The rule is enabled.
To enable detection rules in bulk:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
On the Detection Rules page, select the detection rules you want to enable and click Enable Selected.
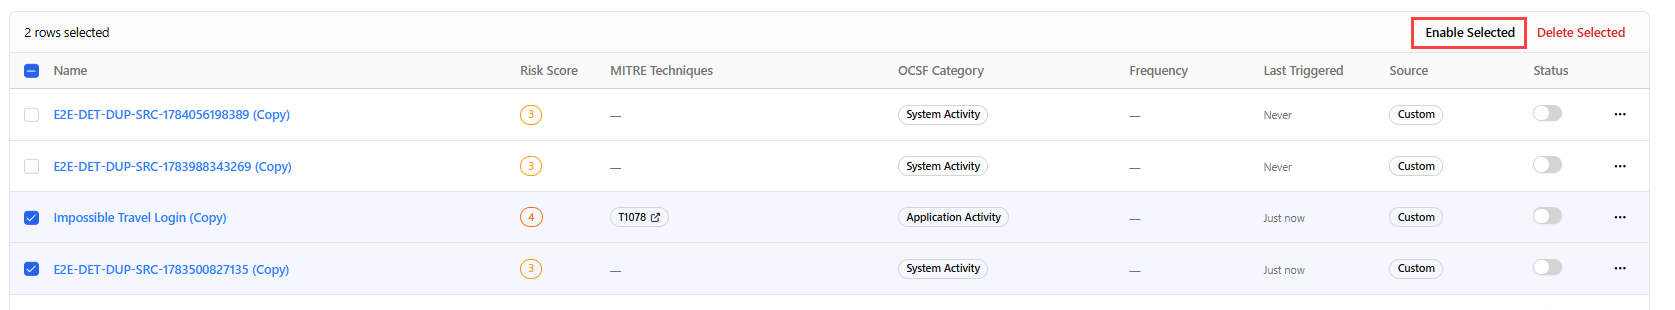
The selected detection rules are enabled.
Deleting Detection Rules
You can delete a detection rule when it's no longer needed. For example, if it has been permanently replaced by another rule or the detection logic is no longer relevant to your environment. Deleting a rule is permanent and cannot be undone, so consider disabling it first if you may want to reuse it later.
You can delete an individual detection rule or in bulk.
-
Only Organization Administrators and the current detection rule owner can delete detection rules.
-
Anomali authored detection rules cannot be deleted.
To delete a detection rule:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
On the Detection Rules page, locate the detection rule you want to delete.
-
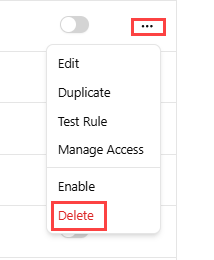
Open the corresponding more options menu (...) and click Delete.
-
In the pop-up message, confirm the deletion by clicking Delete.
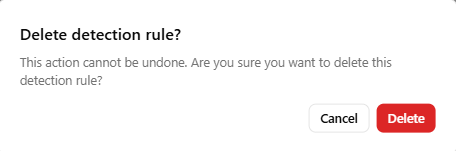
The detection rule is deleted.
To delete detection rules in bulk:
-
Navigate to ThreatStream Next Gen > Security Operations > Detection Rules.
-
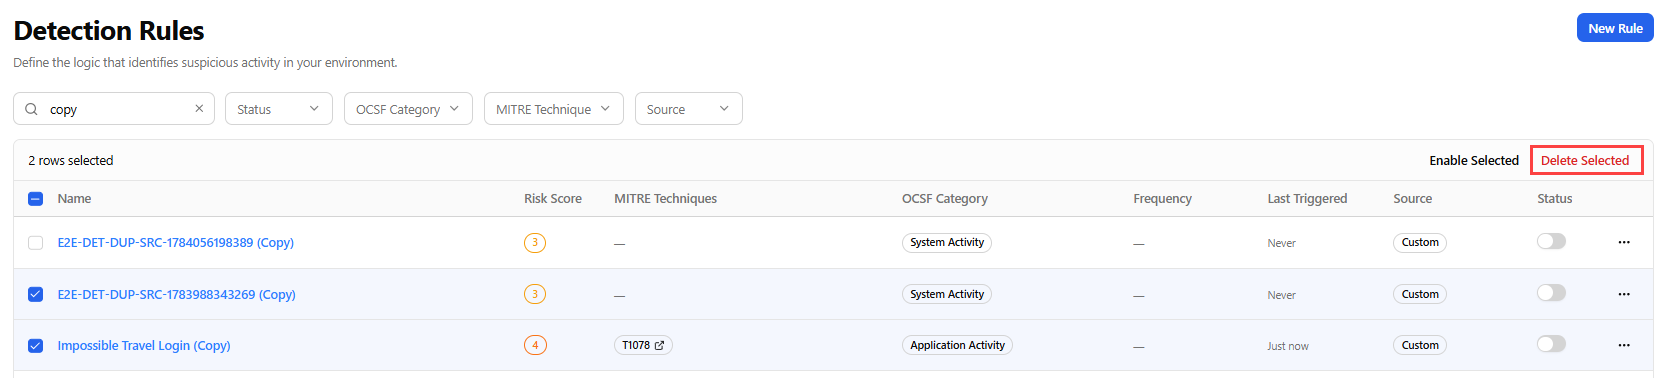
On the Detection Rules page, select the detection rules you want to delete and click Delete Selected.
-
In the pop-up message, confirm the rule deletion by clicking Delete.
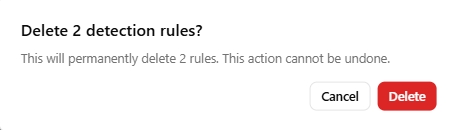
The selected detection rules are deleted.